
When enterprise information sits behind a company firewall or in a personal on-premises information heart, there’s no direct community path from AWS, although the AI brokers and dashboards in Amazon Fast can question nearly any information supply. Directors should be sure that their delicate enterprise information isn’t uncovered to the general public web whereas being accessible for AI-driven insights and actions.
For a lot of enterprises, routing visitors over the general public web introduces unacceptable danger. Regulatory frameworks similar to HIPAA, FedRAMP, and PCI-DSS usually mandate that delicate information stay inside managed community boundaries. Even the place compliance isn’t the first driver, exposing inner information paths will increase the assault floor, complicates audit trails and introduces variable latency that may degrade the person expertise.
This walkthrough reveals you methods to join on-premises information sources to Amazon Fast privately, with out visitors traversing the general public web. It assumes you have already got AWS Direct Join or an AWS Web site-to-Web site VPN linking your on-premises atmosphere to your digital non-public cloud (VPC). From that basis, we configure VPC endpoints powered by AWS PrivateLink in order that Fast can attain your non-public sources over the AWS spine, then layer safety teams and VPC endpoint insurance policies for protection in depth.
By the tip, you’ll have a community structure that retains visitors between Fast and your on-premises information sources off the general public web, lowering the assault floor, offering constant low-latency connectivity, and providing you with a transparent audit path for compliance.
Amazon Fast and establishing non-public community connectivity
Amazon Fast is an AI-powered workspace that brings search, analytics, analysis, and automation right into a single conversational expertise. Understanding which parts attain your non-public community, and the way, determines the structure within the sections that observe.
Information entry in Amazon Fast falls into two paths. Person-facing visitors covers anybody opening the Fast console, interacting with a dashboard, making an API name, or utilizing Fast Desktop. All this routes by way of VPC endpoints (see VPC endpoints for person and API entry), retaining person classes off the general public web.
Information-fetching visitors is when Fast itself reaches into your community to tug information. That is dealt with by VPC connections (see VPC connections for information supply entry), and it’s the place many of the architectural selections lie. The options and integrations that provoke data-fetching connections are:
- Amazon Fast Sight queries on-premises databases (PostgreSQL, MySQL, SQL Server, Oracle, and others) immediately by way of ENIs positioned in your VPC. That is the heaviest client of VPC connections.
- Amazon Fast Flows and Amazon Fast Automate are separate automation options. Flows deal with repeatable duties. Automate handles complicated, multi-system orchestration with human-in-the-loop. Each invoke motion connectors, together with MCP servers hosted privately in your VPC. Any workflow that calls an inner API routes by way of this path.
- Fast Brokers underpin all conversational interactions and might invoke motion connectors immediately. When a customized agent calls a privately hosted MCP server or inner API, visitors flows by way of the VPC connection.
- Amazon Fast Index builds a unified search layer throughout related sources similar to Confluence, SharePoint, and Amazon Easy Storage Service (Amazon S3). For information inside your VPC or on premises, information base VPC connections are at the moment supported just for Amazon Redshift. Sources similar to Confluence, SharePoint, Field, Google Drive, OneDrive, and Amazon S3 can’t use a Fast VPC connection at this time (see Supported VPC information sources). You’ll be able to nonetheless limit Amazon S3 bucket entry to a VPC endpoint by way of a bucket coverage, which is a separate mechanism.
- Amazon Fast Analysis accesses enterprise sources behind the firewall alongside public web information for its citation-backed studies, utilizing the VPC connection when reaching non-public sources.
- Apps in Fast construct interactive internet purposes on prime of structured information and motion connectors, inheriting the identical VPC connectivity as Fast Sight and Flows.
- Fast Areas arrange content material from the previous options however don’t provoke their very own information connections.
These two visitors paths require two distinct non-public connectivity mechanisms that work collectively:
- VPC endpoints (AWS PrivateLink): Deal with user-facing visitors similar to accessing the Fast web site, making API calls, and administrative entry. These hold person visitors off the general public web.
- VPC connections: Deal with information supply visitors. Amazon Fast reaches into your VPC (and by extension, your on-premises community) to fetch information from databases, Amazon Redshift information base sources, and inner APIs. These are configured inside the Fast console.
Configuring non-public connectivity
This part walks by way of the 4 constructing blocks so as: VPC endpoints for person and API entry, VPC connections for information supply entry, VPC endpoints for AWS information companies, and outbound entry to required exterior domains.
Conditions
Earlier than configuring non-public connectivity for Fast, be sure that the next are in place:
- An energetic AWS account with an Amazon Fast Enterprise subscription (VPC connections require Enterprise version).
- An current VPC within the AWS Area the place Fast is deployed.
- A supported AWS Area. Fast web site VPC endpoints will not be accessible within the AWS China Areas or the AWS GovCloud (US) Areas.
- An AWS Direct Join connection or Web site-to-Web site VPN established between your on-premises community and your VPC. That is the non-public path that carries visitors out of your information heart into AWS.
- AWS Identification and Entry Administration (IAM) permissions to create and handle VPC endpoints, safety teams, and Fast administration. To create VPC connections, the administrator’s IAM identification additionally wants
quicksight:CreateVPCConnection,quicksight:DescribeVPCConnection,quicksight:ListVPCConnections,quicksight:UpdateVPCConnection,quicksight:DeleteVPCConnection,ec2:DescribeSubnets,ec2:DescribeVpcs,ec2:DescribeSecurityGroups,iam:ListRoles, andiam:PassRolescoped to the VPC connection execution position. - Entry to your group’s DNS administration (Route 53 non-public hosted zones or on-premises DNS forwarders), as non-public DNS decision routes visitors by way of VPC endpoints slightly than public addresses.
VPC endpoints for person and API entry (AWS PrivateLink)
VPC endpoints powered by PrivateLink deal with all user-facing visitors to Amazon Fast, together with the web site, API calls, and embedded content material. They forestall customers from needing to traverse the general public web to entry the Amazon Fast console.
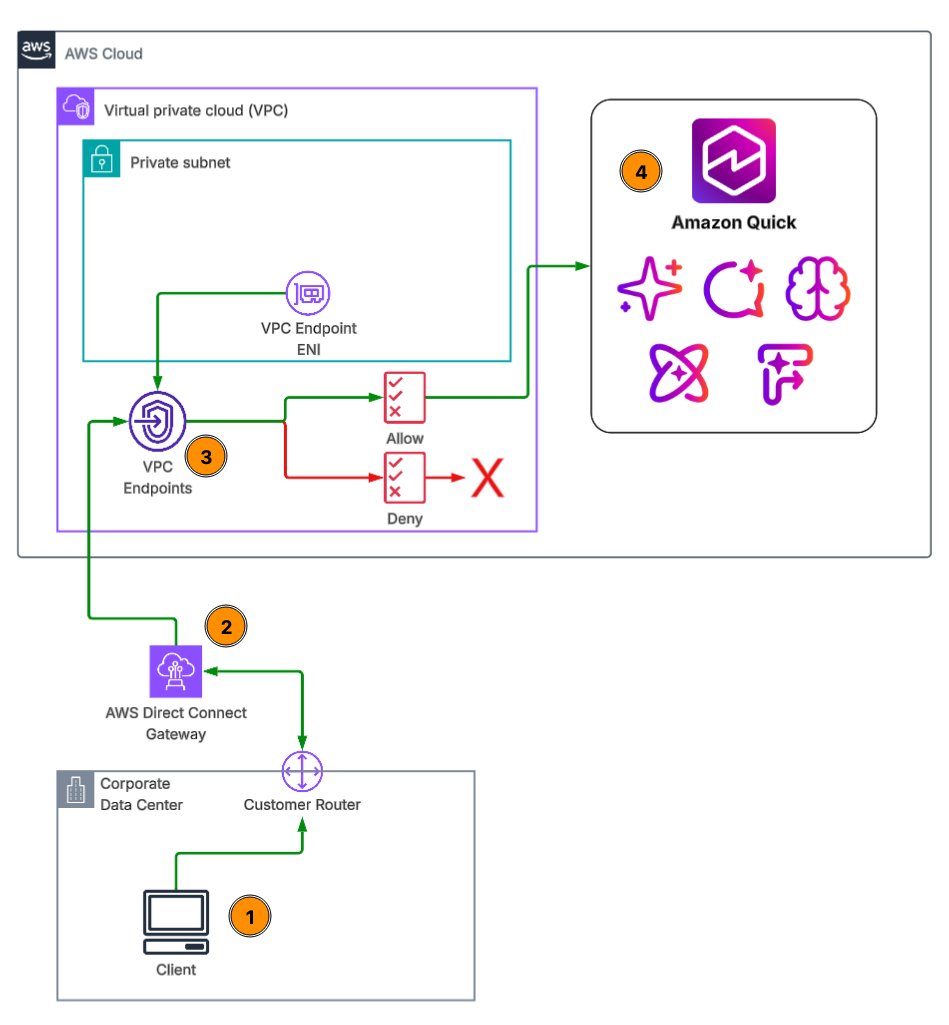
Determine 1: Non-public entry to Amazon Fast from a company information heart by way of a VPC endpoint
As proven in Determine 1: (1) a consumer on the company community sends a request to Fast; (2) the request travels over AWS Direct Join, by way of the Direct Join gateway, into your VPC; (3) the Fast VPC endpoint evaluates the endpoint coverage and permits or denies the request; (4) allowed requests attain Amazon Fast over the AWS community.
Planning your VPC endpoint structure
When planning your endpoint structure, start by figuring out the AWS Area the place your Fast account is deployed, as VPC endpoints should be in the identical Area. Select subnets throughout a number of Availability Zones for endpoint ENI placement, and ensure these subnets have routes to your on-premises community by way of Direct Join or VPN.
Design safety teams that limit visitors on the endpoint ENIs to solely required ports and supply ranges. If you need all visitors routed privately (together with the calls Amazon Fast makes to Amazon S3, Amazon Redshift, and Amazon Athena), plan VPC endpoints for these companies as effectively (see Configuring information supply VPC endpoints).
Creating VPC endpoints for Fast
Fast requires two interface VPC endpoints for full non-public entry:
- Web site entry endpoint – Service title
com.amazonaws.. This handles the majority of person visitors to the Fast console. Non-public DNS names for the Fast web site differ from the general public URL, so you have to create an A document for.quicksight-website .quicksight.aws.amazon.com - API entry endpoint – Service title
com.amazonaws.. This handles programmatic API calls. When non-public DNS is enabled, current API calls to.quicksight quicksight.robotically route by way of the VPC endpoint with no extra DNS configuration. For FIPS compliance, use.amazonaws.com com.amazonaws...quicksight-fips
Observe: Not each Fast API is accessible by way of the API VPC endpoint. The next 13 APIs will not be supported: the motion connector APIs (CreateActionConnector, DeleteActionConnector, DescribeActionConnector, DescribeActionConnectorPermissions, ListActionConnectors, SearchActionConnectors, UpdateActionConnector, UpdateActionConnectorPermissions) and the stream APIs (GetFlowMetadata, GetFlowPermissions, ListFlows, SearchFlows, UpdateFlowPermissions). Automation that manages motion connectors or flows programmatically wants a path to the general public API endpoint. See Fast and interface VPC endpoints.
If directors register to Amazon Fast as IAM customers by way of the VPC, additionally create the AWS Administration Console endpoints:
com.amazonaws...console com.amazonaws...signin
To create the web site endpoint within the Amazon Digital Non-public Cloud (Amazon VPC) console:
- Open the Amazon VPC console. Within the navigation pane, underneath PrivateLink and Lattice, select Endpoints, then select Create endpoint.
- Enter a Identify tag (for instance, my-quicksight-vpc-endpoint) and, for Sort, select AWS companies.
- Underneath Providers, seek for
com.amazonaws.and choose.quicksight com.amazonaws.(Determine 2)..quicksight-website
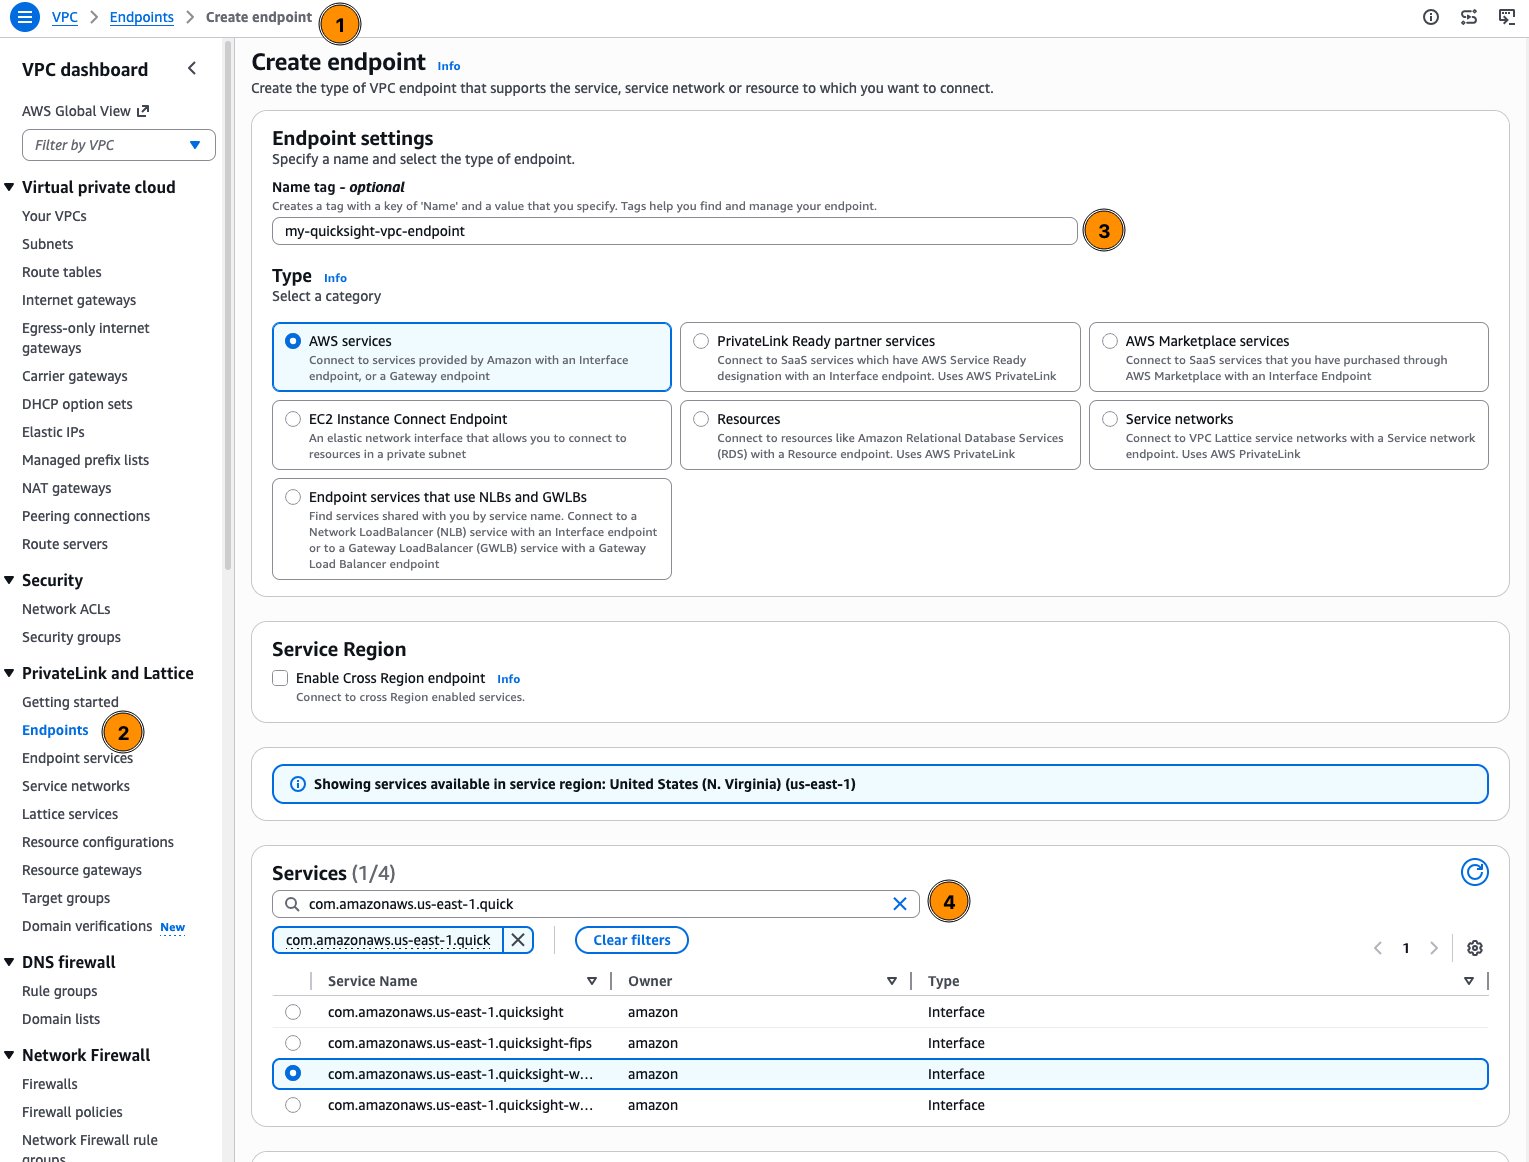
Determine 2: Naming the endpoint and deciding on the Fast web site endpoint service
- Underneath Community settings, choose your VPC. Underneath Extra settings, hold Allow non-public DNS title chosen.
- Choose subnets in at the least two Availability Zones, then choose the safety group for the endpoint ENIs (Determine 3).
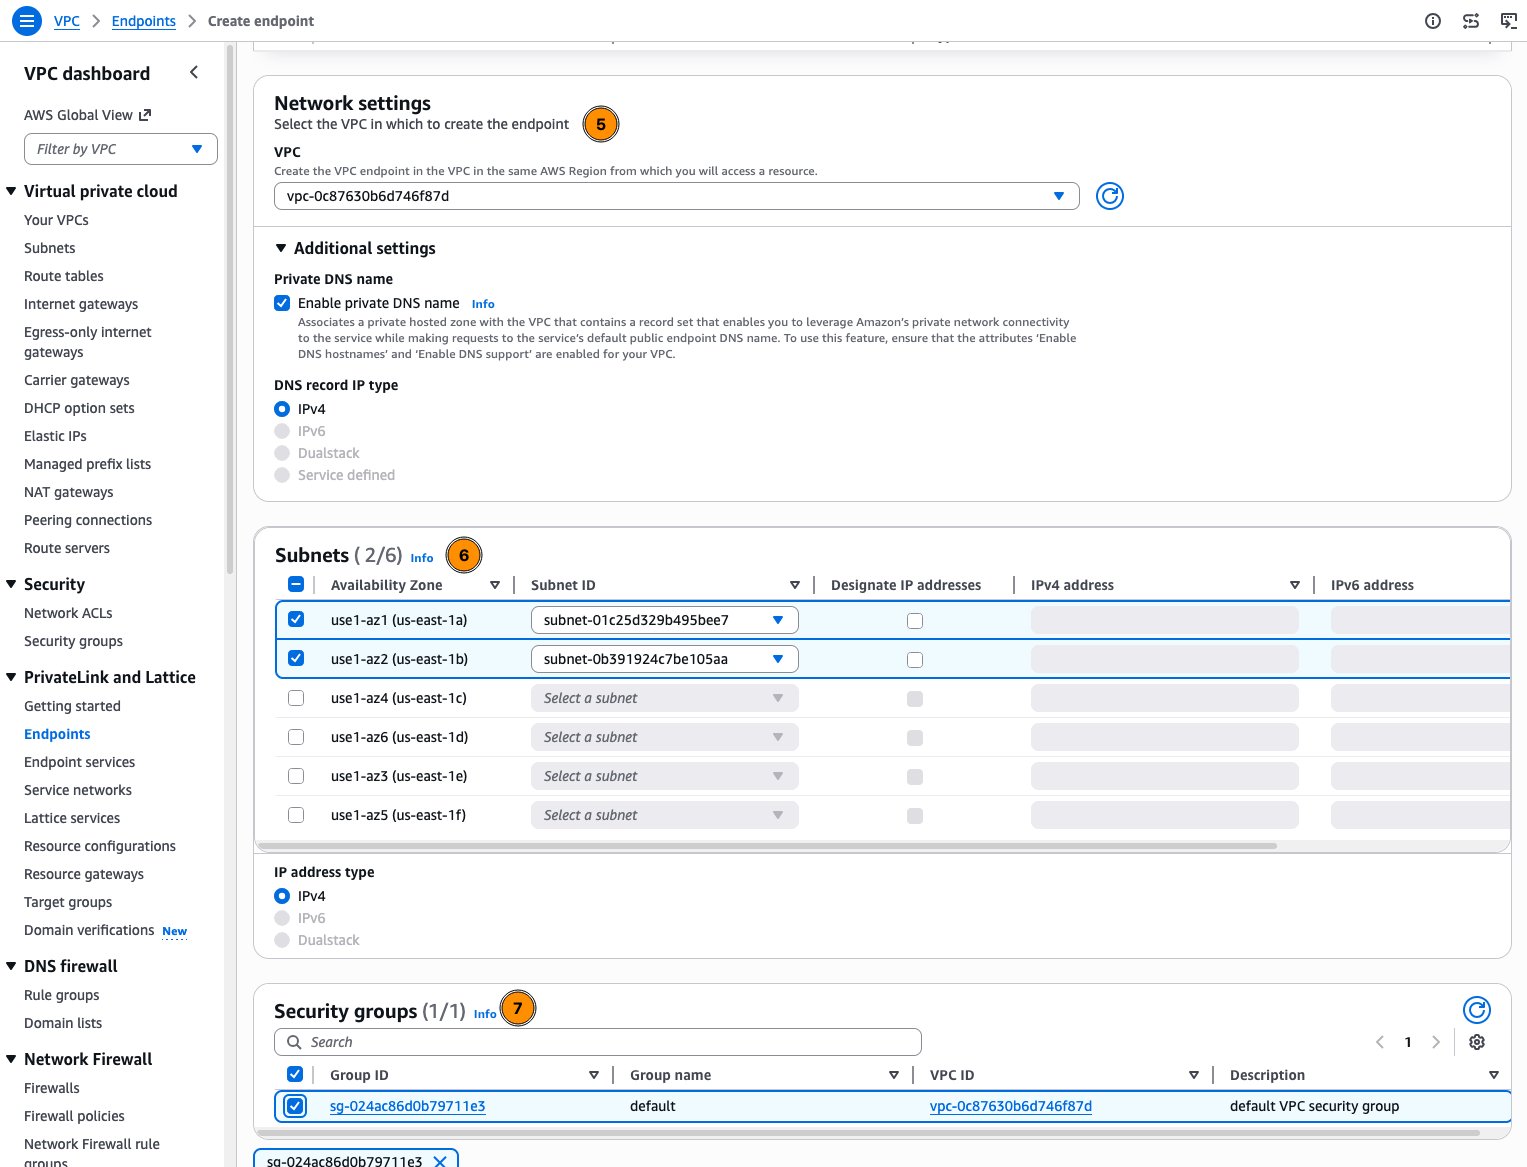
Determine 3: Deciding on the VPC, non-public DNS, subnets, and safety group for the endpoint
- Select a Coverage (see the next Organising VPC endpoint insurance policies part), add tags, and select Create endpoint (Determine 4).
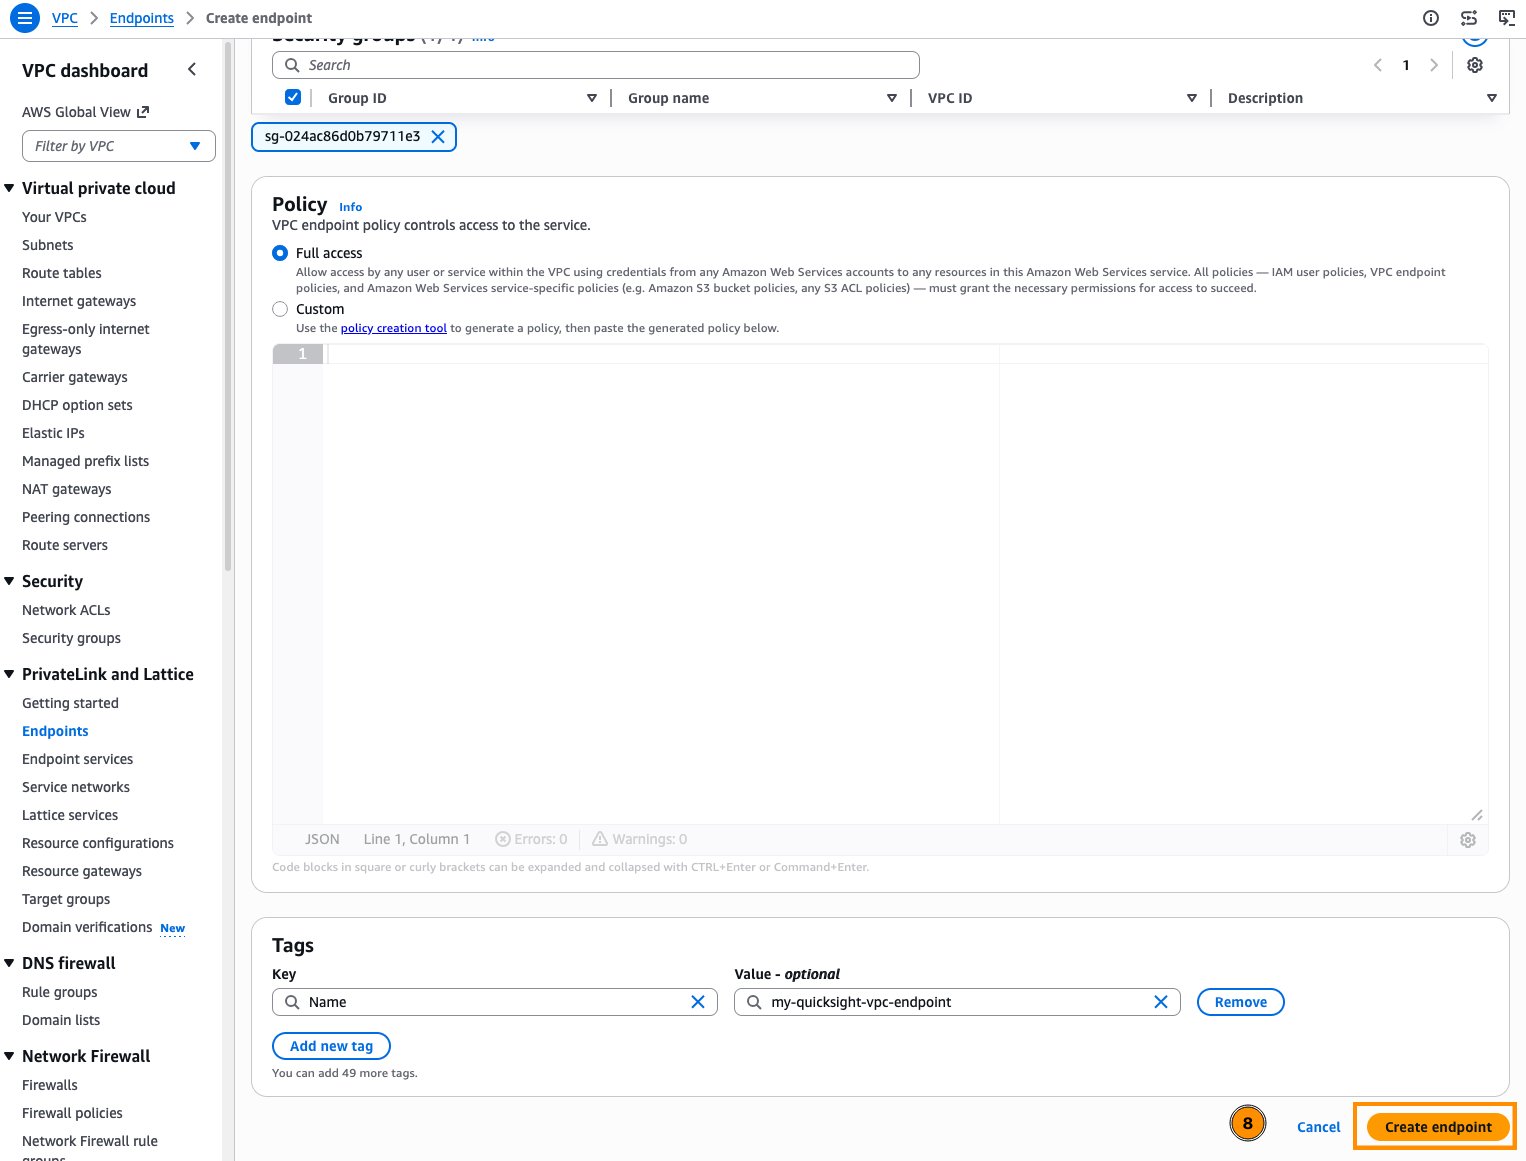
Determine 4: Selecting the endpoint coverage and creating the endpoint
- Repeat these steps for the API endpoint,
com.amazonaws...quicksight
Configuring DNS decision
For the web site endpoint, create an A document for
A Route 53 non-public hosted zone solely solutions queries from contained in the VPCs related to it. As a result of your customers join from the company community, configure your on-premises DNS servers to ahead queries for
To create the document in Route 53:
- Within the Route 53 console, select Hosted zones, then Create hosted zone.
- For Area title, enter
.quicksight.aws.amazon.com us-east-1.quicksight.aws.amazon.com). Scoping the zone to your Area avoids overriding different Fast host names. Select Non-public hosted zone, affiliate your VPC, and select Create hosted zone (Determine 5).
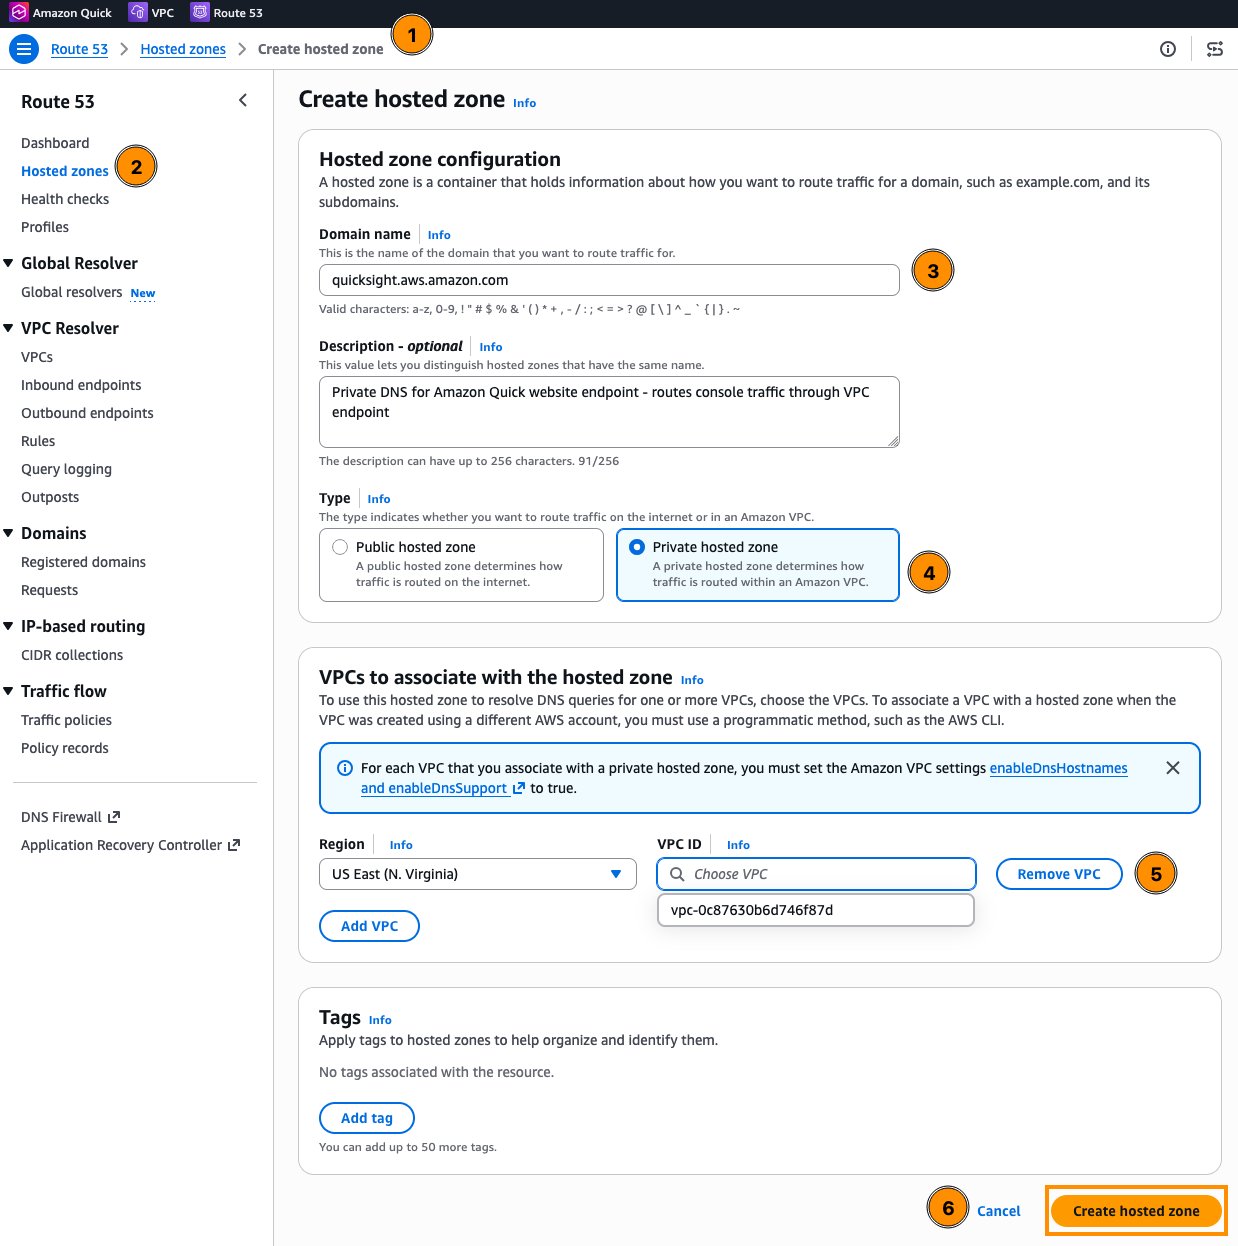
Determine 5: Creating a personal hosted zone in Amazon Route 53
- Within the new hosted zone, select Create document (Determine 6).
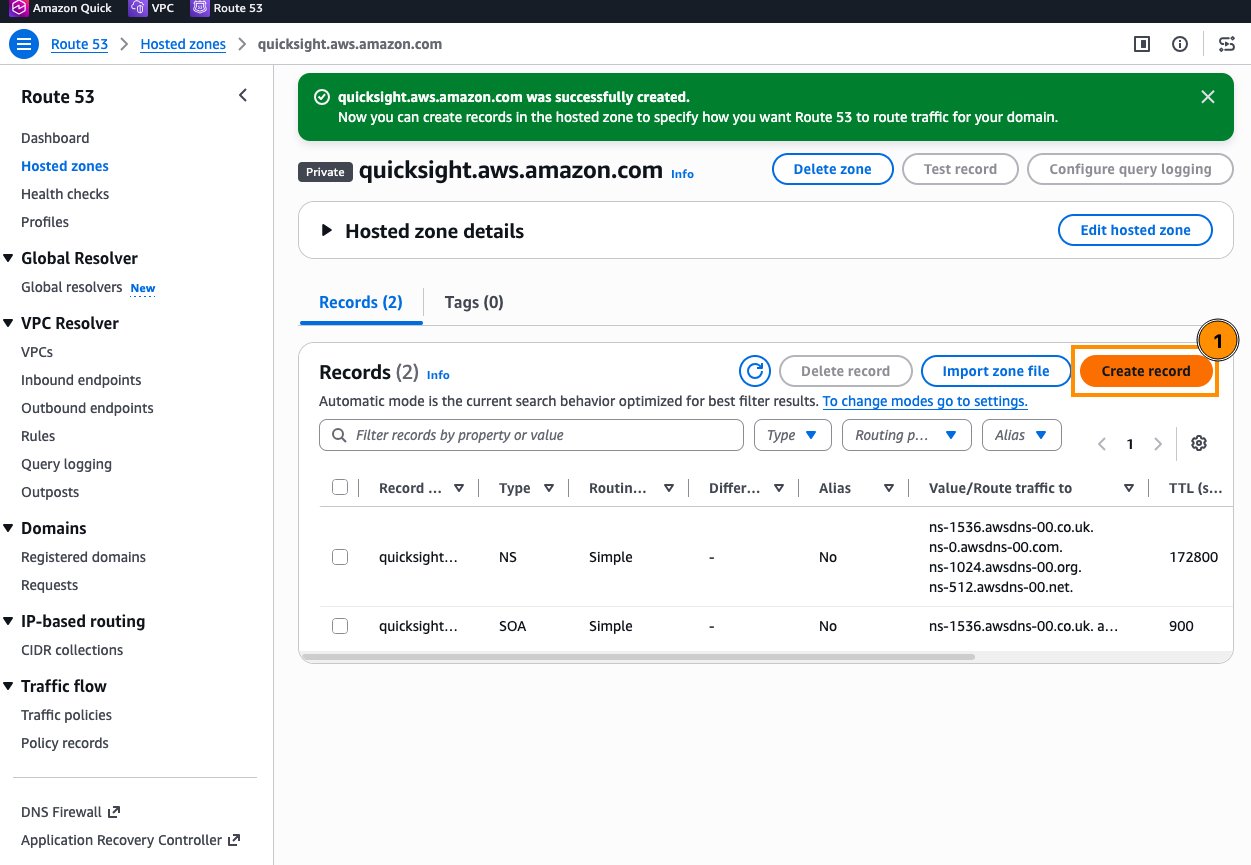
Determine 6: Making a document within the new non-public hosted zone
- Go away Report title clean, select document sort A, activate Alias, select Alias to VPC endpoint, choose your Area and the web site endpoint’s DNS title, and select Create information (Determine 7).
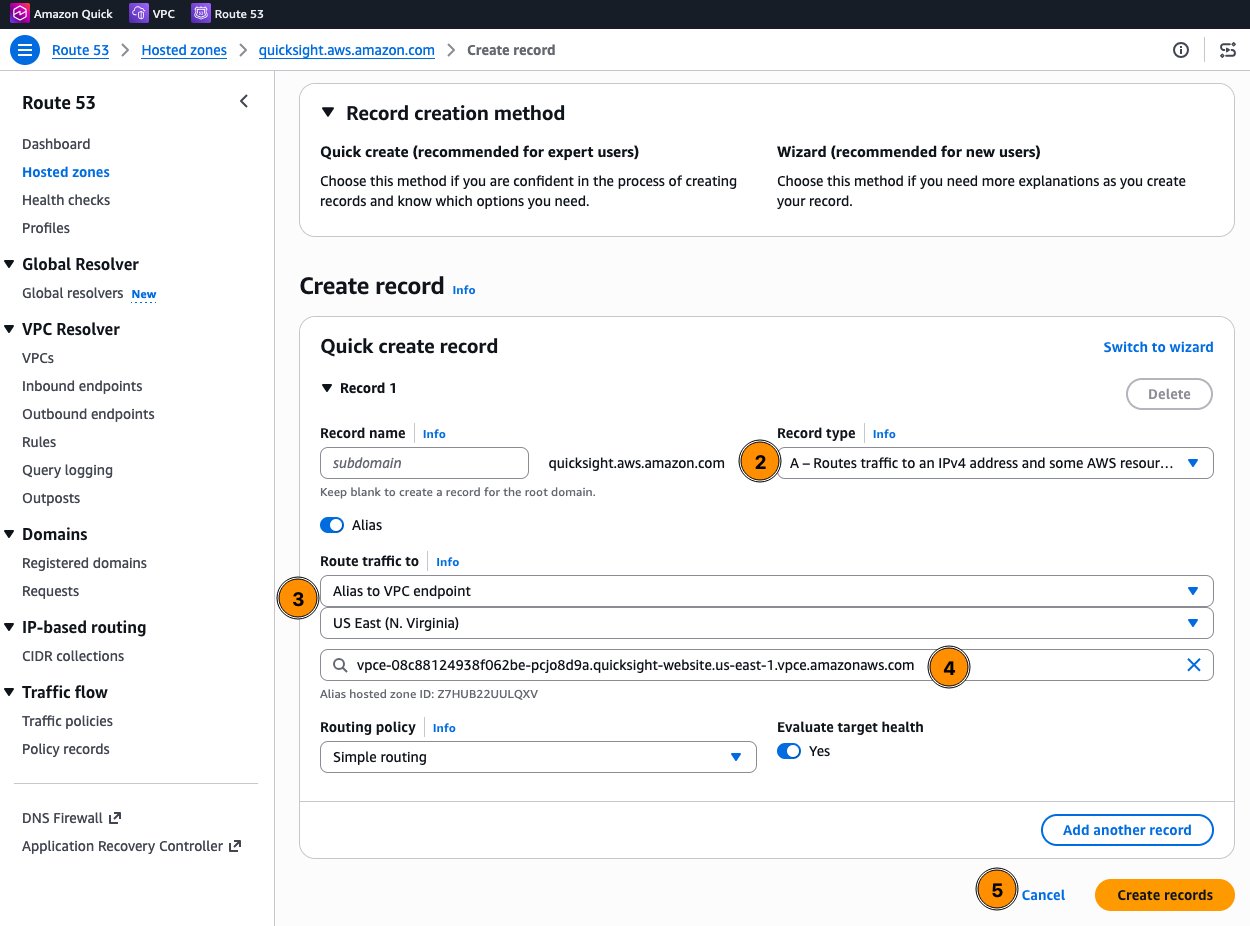
Determine 7: Creating an alias A document that factors to the Fast web site VPC endpoint
Organising VPC endpoint insurance policies
VPC endpoint insurance policies limit which accounts or organizations can use the endpoint. For Fast, insurance policies may be scoped by AWS account ID or Group ID. To vary a coverage, open the endpoint within the Amazon VPC console, select the Coverage tab, and select Edit Coverage (Determine 8).
Vital limitation: For the Fast web site endpoint, the
Principal,Motion, andUseful resourcefields should all be set to*. Circumstances would possibly solely be specified towards theaws:PrincipalAccountoraws:OrgIdattributes. Extra restrictive action-level insurance policies are solely supported on the API endpoint.
Web site endpoint coverage instance:
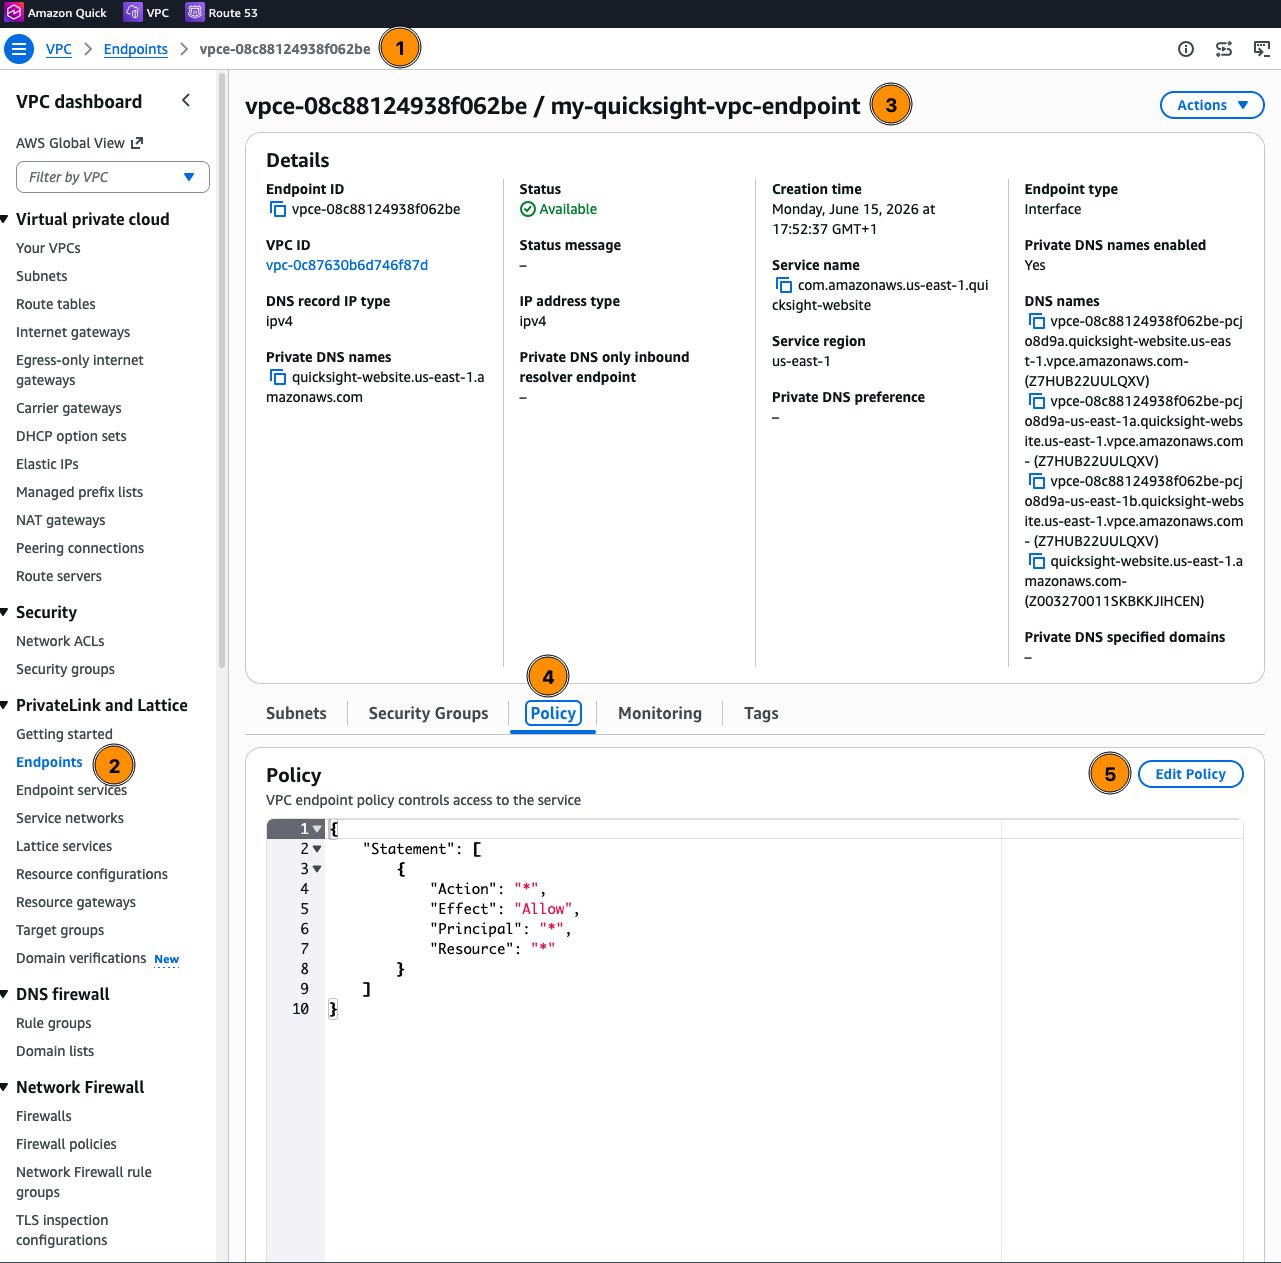
Determine 8: Opening the endpoint coverage from the VPC endpoint particulars web page
API endpoint coverage instance (restricted to particular actions):
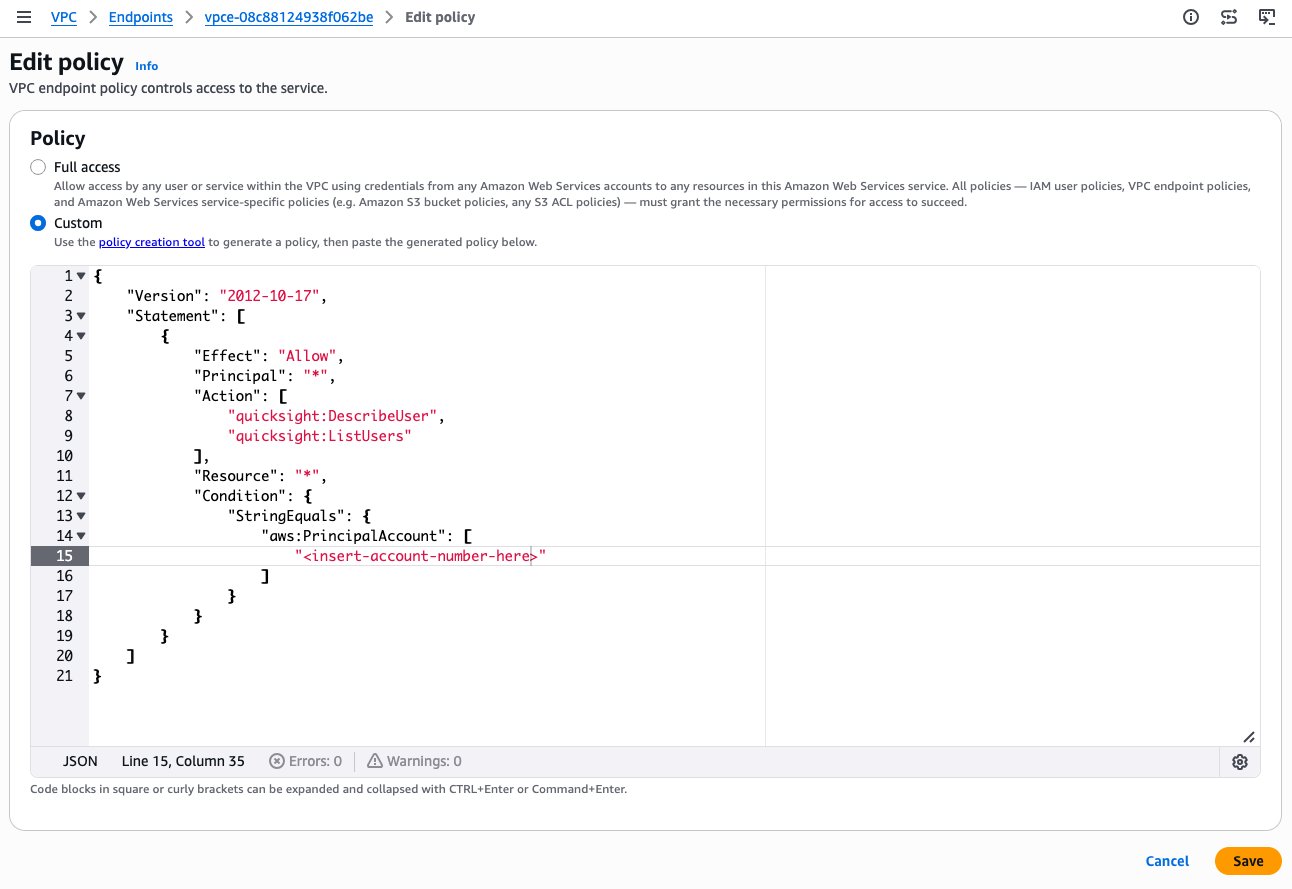
Determine 9: Modifying a customized VPC endpoint coverage
VPC connections for information supply entry
Whereas VPC endpoints deal with user-facing visitors, VPC connections deal with the server-side path, that means Amazon Fast reaches into your VPC to entry databases, Amazon Redshift information base sources, and inner APIs.
How VPC connections work
Amazon Fast Enterprise version is totally built-in with Amazon VPC. If you create a VPC connection in Amazon Fast, you might be including elastic community interfaces (ENIs) into your VPC subnets. These ENIs permit Fast to alternate community visitors with sources inside your VPC and, by extension, something reachable from that VPC, together with on-premises methods related by way of Direct Join or VPN.
All customary VPC safety controls apply to this visitors. Route tables, community ACLs, subnets, and safety teams govern visitors to and from Fast in the identical method they govern visitors between every other situations in your VPC. This implies you’ll be able to connect with:
- Non-public databases not uncovered to the general public web.
- On-premises information sources reachable by way of Direct Join or VPN.
- Inner APIs accessible by IP deal with inside your community.
Create a devoted safety group (for instance, QuickSight-VPC) for the VPC connection ENIs. On every information supply’s safety group, permit inbound visitors on the database port from that safety group ID.
Observe for VPC connections created earlier than April 27, 2023: The safety group connected to the Fast community interface just isn’t stateful. You should add an inbound rule that explicitly permits return visitors out of your information supply’s safety group on all ports (0–65535), as a result of return packets use randomly allotted vacation spot ports. Connections created after that date use customary stateful habits. See Safety teams: inbound and outbound guidelines.
Creating the execution position
Amazon Fast doesn’t create the VPC connection execution position for you. Earlier than you add the connection, create a devoted IAM position (advisable), or replace an current position that already trusts Fast, similar to aws-quicksight-service-role-v0 used within the screenshots on this submit. The position wants:
- A permissions coverage that grants the Amazon Elastic Compute Cloud (Amazon EC2) actions Fast makes use of to handle its ENIs (Determine 10).
- A belief coverage that permits
quicksight.amazonaws.comto imagine the position. Solely roles with this belief coverage seem within the Execution position checklist within the Fast console.
Permissions coverage:
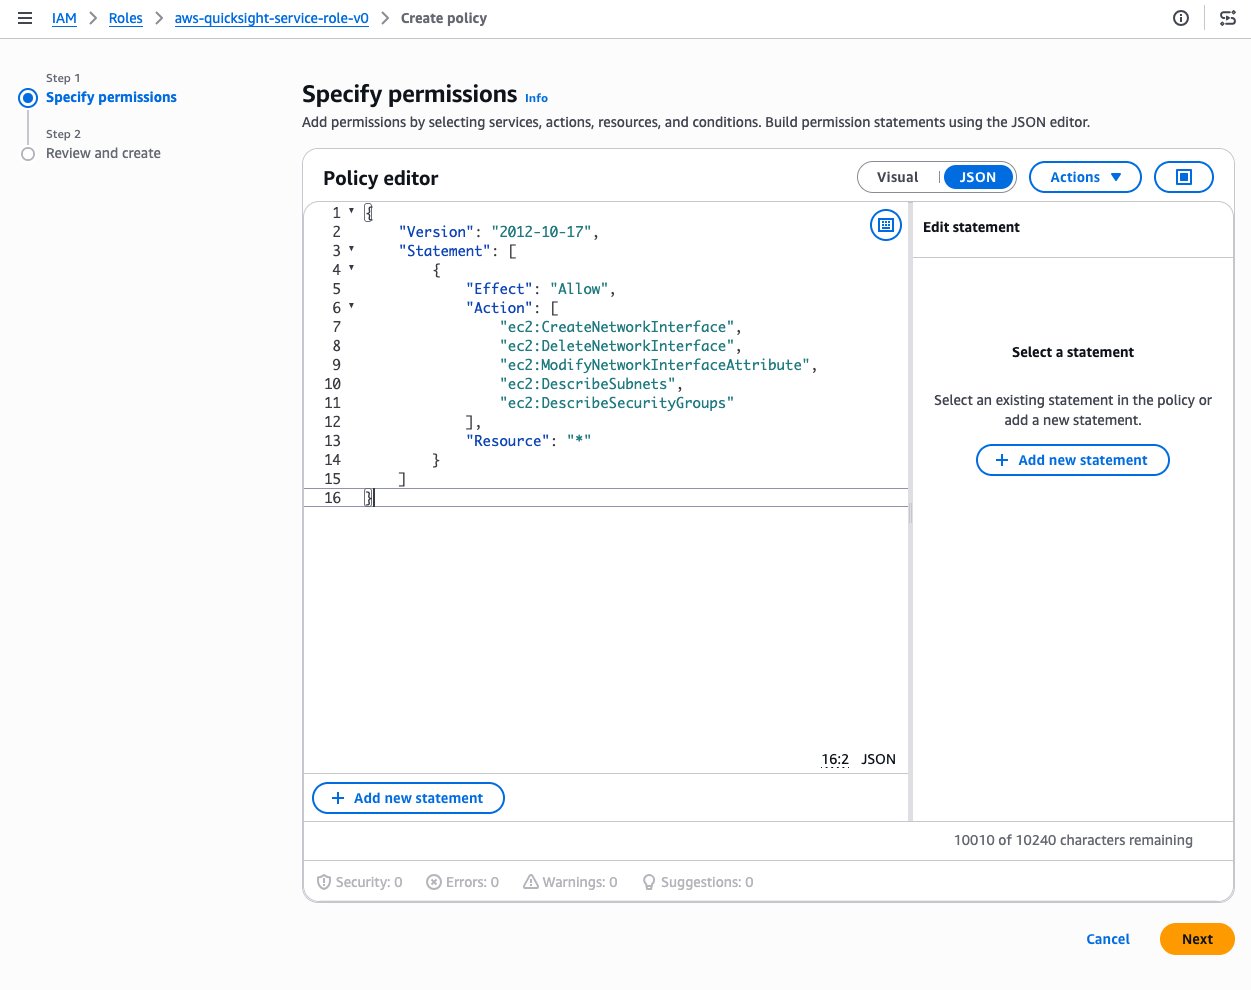
Determine 10: Including the Amazon EC2 permissions required by the VPC connection execution position
Belief coverage:
Configuring a VPC connection
To create a VPC connection within the Fast console:
- Check in to Amazon Fast as an administrator. Select your profile icon within the upper-right, then select Handle account (Determine 11). Should you don’t see this selection, you’re not a Fast administrator.
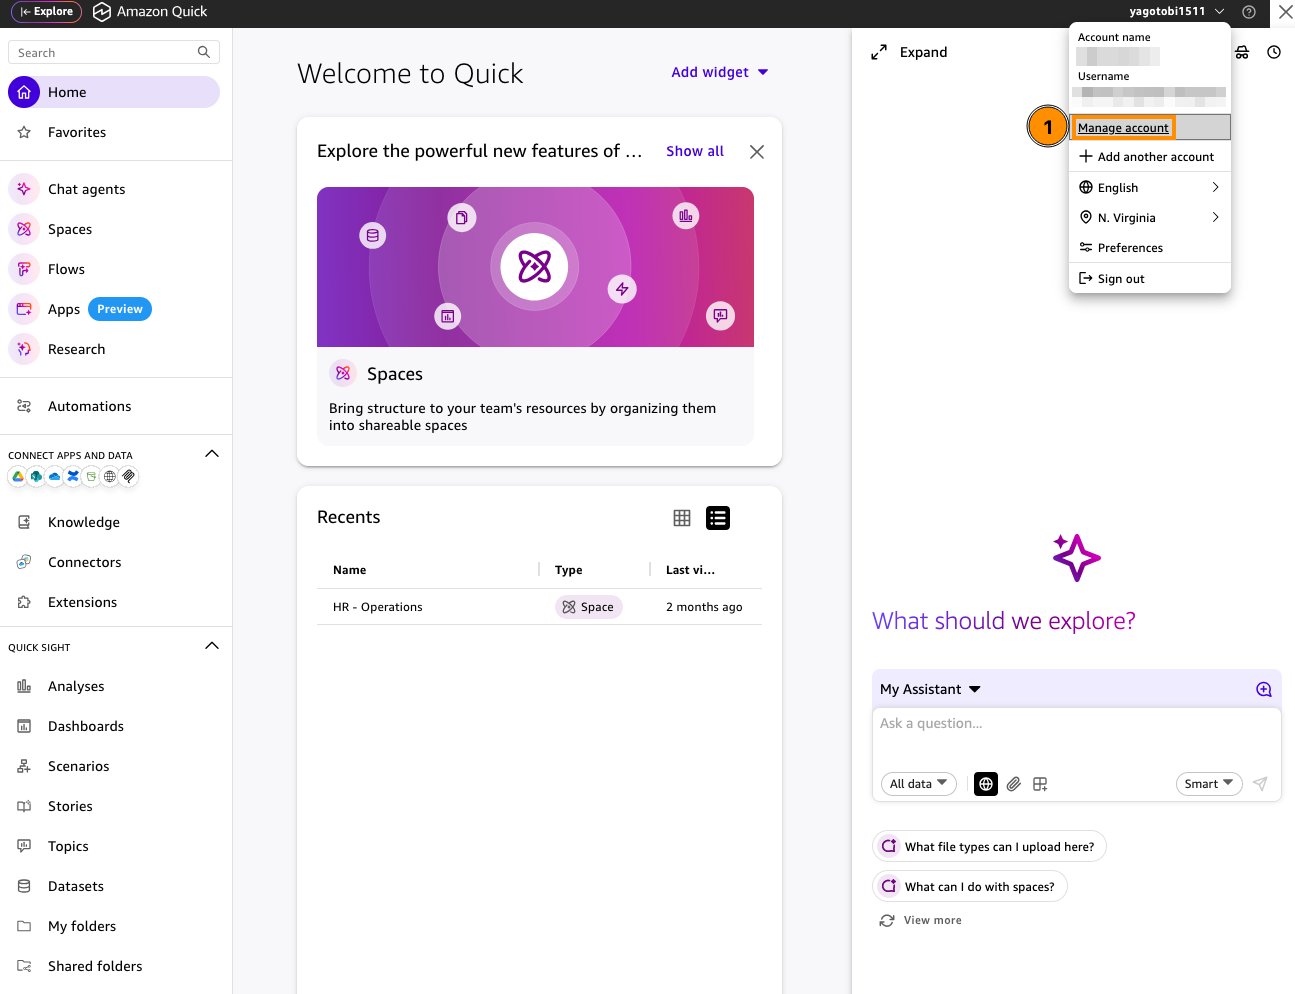
Determine 11: Opening Handle account from the Fast profile menu
- Within the navigation pane, underneath Safety, select Handle VPC connections (Determine 12), then select Add VPC connection.
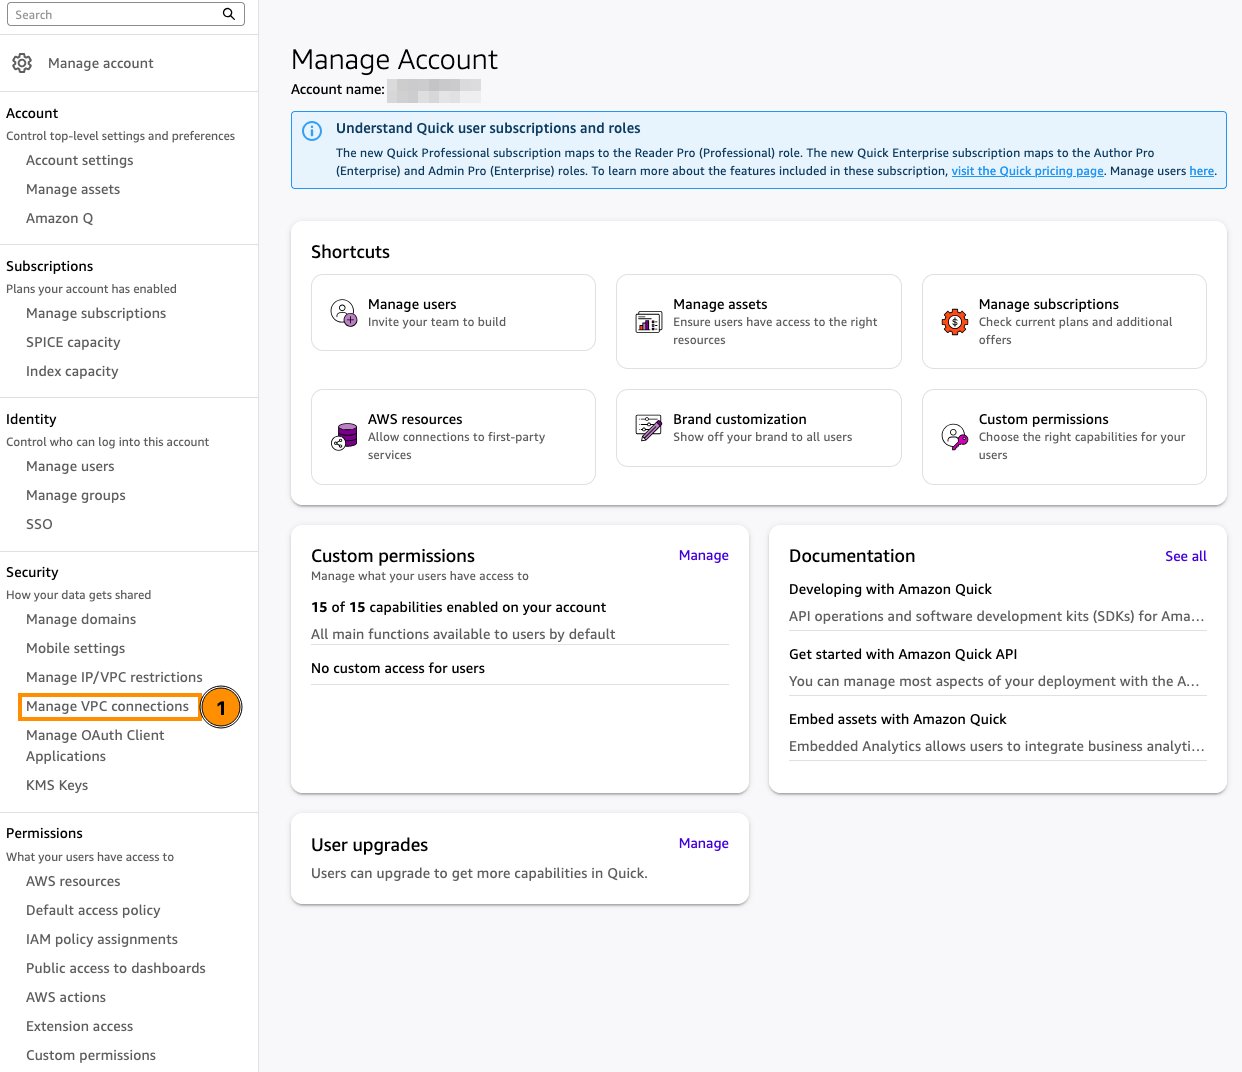
Determine 12: Handle VPC connections underneath Safety on the Handle account web page
- Present the next (Determine 13):
- A descriptive VPC connection title.
- The VPC ID of the goal VPC. This could’t be modified later.
- The Execution position you created within the earlier step.
- At the very least two subnets in numerous Availability Zones.
- At the very least one safety group ID.
- (Elective) In case your database host title should be resolved by way of non-public DNS, enter the IP addresses of your Route 53 Resolver inbound endpoints underneath DNS resolver endpoints.
- Select ADD.
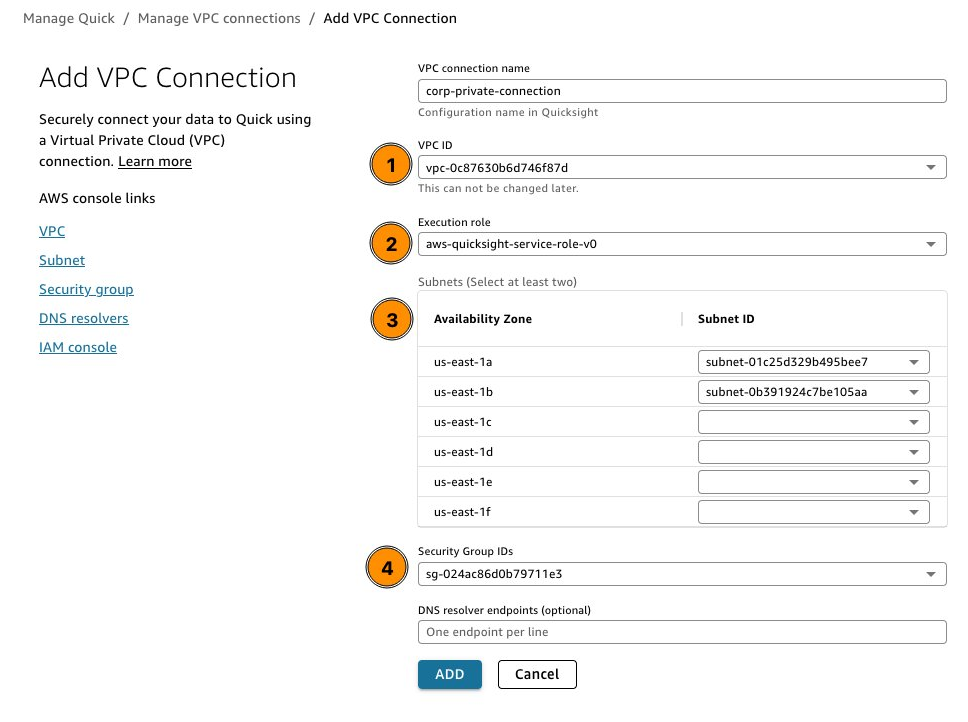
Determine 13: Including a VPC connection within the Fast console
The connection standing reveals UNAVAILABLE till Fast finishes provisioning the ENIs, then adjustments to AVAILABLE. A standing of PARTIALLY AVAILABLE means one of many ENIs is unavailable, however the connection can nonetheless be used.
Configuring information supply VPC endpoints
VPC endpoints (PrivateLink, used right here for AWS service APIs) and VPC connections (Fast ENIs positioned in your VPC; see VPC connections for information supply entry) are totally different mechanisms. Fast accesses different AWS companies (Amazon S3, Amazon Redshift, Amazon Athena, AWS Secrets and techniques Supervisor) when retrieving information for dashboards and analytics. If you need all visitors to stay non-public, together with the calls Amazon Fast makes to those AWS companies, create interface or gateway VPC endpoints for every:
| Service | Endpoint sort | Service title |
| Amazon S3 | Gateway | com.amazonaws. |
| Amazon Redshift | Interface | com.amazonaws. |
| Amazon Athena* | Interface | com.amazonaws. |
| AWS Secrets and techniques Supervisor | Interface | com.amazonaws. |
| AWS Glue | Interface | com.amazonaws. |
* Athena isn’t supported as a VPC connection information supply. The Athena endpoint retains Athena API visitors on AWS PrivateLink solely.
Create these endpoints in the identical VPC the place the Amazon Fast ENIs are positioned. Ensure that route tables and safety teams permit visitors between the Amazon Fast subnets and the endpoint subnets.
Enabling entry to required exterior domains
Whereas information visitors between Fast and your on-premises sources stays on the non-public community, customers’ browsers nonetheless want to achieve a set of domains for sign-in, static belongings, client-side metrics, and integrations. Even with VPC endpoints configured, domains with out VPC endpoint help want outbound connectivity, usually by way of your company proxy or firewall. In case your account makes use of IAM Identification Heart, browser sign-in additionally requires the general public AWS sign-in and IAM Identification Heart endpoints (see Safe person entry and identification federation).
Required exterior domains
| Area | Objective | VPC endpoint help |
|
Bulk of Fast web site visitors | Sure |
quicksight. |
Fast public API calls | Sure |
signin.aws.amazon.com |
AWS console sign-in for accounts that use IAM identities | Sure |
|
Signal-in | No |
*.cloudfront.web |
Static belongings (CSS, JavaScript) | No |
*.s3. |
Experiences and thumbnails | Sure |
*.execute-api. |
Shopper-side metrics | No |
*.kinesisvideo.amazonaws.com |
Dwell streaming of automation workflows | No |
apis.google.com/js/api.js |
Google Drive file picker | N/A |
*.officeapps.reside.com |
Fast aspect panel extension | N/A |
outlook.cloud.microsoft |
Fast aspect panel extension | N/A |
*.sharepoint.com |
Fast aspect panel extension | N/A |
*.workplace.com |
Fast aspect panel extension | N/A |
*.office365.com |
Fast aspect panel extension | N/A |
Supply: Domains accessed by Fast.
Configuration steering:
- For domains with VPC endpoint help (the Fast web site and API,
signin.aws.amazon.com, and Amazon S3), create the corresponding VPC endpoints and DNS information. - For domains with out VPC endpoint help, permit them by way of your company web egress (outbound proxy or firewall). If person visitors egresses by way of your VPC, use a NAT gateway in a public subnet.
- In case your safety posture requires URL-level filtering, use an outbound proxy or AWS Community Firewall area filtering guidelines to permit solely the domains listed earlier.
- Take a look at from a company workstation (or an occasion in the identical egress path):
nslookupandcurltowards every area verify DNS decision and routing.
Imposing VPC endpoint restrictions
After your endpoints are configured and examined, you’ll be able to implement that each one entry to your Fast account should come by way of the VPC endpoint, blocking normal web entry completely. In consequence, customers can solely attain Fast out of your company community by way of the non-public path you’ve established.
Fast gives IP and VPC endpoint restriction controls that restrict account entry to a predefined checklist of IP ranges, VPC IDs, or VPC endpoint IDs. For instance, you’ll be able to create a rule that permits entry solely from the VPC endpoint used for Direct Join, that means anybody trying to achieve Fast from the general public web will probably be denied.
To configure by way of the Fast console (solely directors signed in with IAM credentials can entry the restrictions web page):
- Select your profile icon, then Handle account. Underneath Safety, select Handle IP/VPC restrictions.
- Within the Restriction area, enter the VPC endpoint ID (for instance,
vpce-001122def), enter a Description, and select Add (Determine 14). - Select Save adjustments to use the rule.
- Activate Implement restrictions.
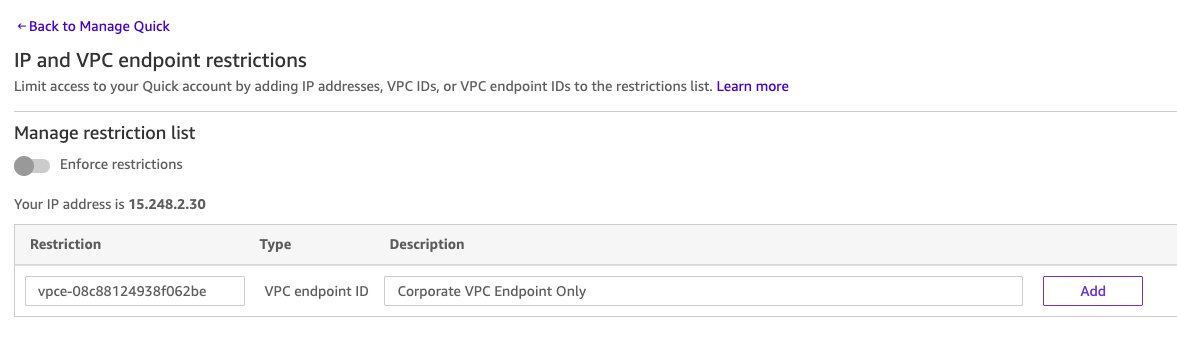
Determine 14: Including a VPC endpoint rule on the IP and VPC endpoint restrictions web page
Alternatively, configure by way of the AWS Command Line Interface (AWS CLI):
Observe:
UpdateIpRestrictionreplaces your complete rule map. Retrieve your present guidelines withaws quicksight describe-ip-restrictionand embody any current guidelines within the replace.
Key concerns:
- IP and VPC endpoint guidelines apply to Fast internet, embedded, and cellular entry, that means they don’t limit entry to the general public API. To limit API calls from particular sources, use IAM insurance policies with
aws:SourceIporaws:SourceVpcecircumstances. - Ensure that your individual IP or VPC endpoint is included within the guidelines earlier than enabling restrictions, in any other case you’ll lock your self out.
- Guidelines can take as much as 10 minutes to take full impact.
- You’ll be able to mix IP guidelines and VPC endpoint guidelines, such that visitors is allowed if it satisfies both rule sort. You’ll be able to add as much as 100 IP and VPC endpoint guidelines mixed.
- IP and VPC endpoint guidelines are enforced throughout all AWS Areas on your account, however you’ll be able to solely add or handle them from the AWS Area the place your Fast account was created.
- In case you have publicly embedded dashboards, they’ll solely be accessible by way of the VPC endpoint as soon as restrictions are enabled.
After you implement the restrictions, solely visitors arriving by way of the desired VPC endpoint (or allowed IP ranges) can attain your Fast account. All different entry is denied.
Safe person entry and identification federation
Non-public community connectivity retains visitors off the general public web, however it doesn’t reply the query of who can entry what inside Fast. This part covers methods to combine your company identification supplier, management person provisioning, and implement fine-grained entry segmentation throughout Fast parts.
Integrating with AWS IAM Identification Heart
Vital: For Fast accounts built-in with IAM Identification Heart, browser-based authentication requires entry to the general public AWS sign-in and IAM Identification Heart endpoints. VPC endpoints don’t present this browser sign-in path. Public IP addresses aren’t required. Present outbound connectivity by way of a NAT gateway or proxy. See Concerns for personal entry within the IAM Identification Heart Person Information.
Amazon Fast makes use of AWS IAM Identification Heart because the central level for workforce identification administration. IAM Identification Heart connects to your current company identification supplier (IdP) utilizing SAML 2.0 for authentication and SCIM 2.0 for computerized person and group provisioning. This gives:
- Computerized person provisioning and deprovisioning synced out of your IdP.
- Group membership synchronization – when a person is added to or faraway from a bunch, that change propagates to Fast.
- Single sign-on (SSO) utilizing current company credentials.
- Momentary credentials by way of assumed IAM roles – no long-lived Fast-specific passwords.
For a step-by-step information on organising IAM Identification Heart along with your identification supplier, see Getting began with IAM Identification Heart.
Position-based entry in Fast
Fast helps three base roles that decide what a person can do:
- Admin – Full administration entry together with information supply configuration, VPC connections, safety settings, person administration, and SPICE capability buying.
- Creator – Can create and publish dashboards, construct brokers, configure Areas, handle information sources, create flows, and construct apps.
- Reader – Can view printed dashboards, work together with brokers, use Areas they’ve been granted entry to, and eat Fast Analysis studies.
These roles are mapped to IAM roles that federated customers assume at sign-in. By managing position project in your IdP, you preserve a single supply of reality for who has what stage of entry.
Moreover, Fast helps customized permissions profiles that may override default position permissions on the account, position, or person stage. Person-level permissions override role-level, which in flip override account-level. This provides directors granular management past the three base roles.
Person segmentation with Areas
Fast Areas present a further layer of entry segmentation past roles. Every House may be configured with particular person and group permissions, that means:
- A finance workforce House containing delicate income dashboards and monetary information bases is simply accessible to the finance group.
- A gross sales workforce House with CRM-connected brokers and pipeline dashboards is restricted to gross sales customers.
- Cross-functional Areas may be shared throughout a number of teams with acceptable permissions.
House-level entry is managed by the teams synced out of your identification supplier, so including a brand new workforce member to the suitable group robotically grants them entry to the related Areas.
Row-level safety in Fast Sight
For dashboards backed by structured information, Fast Sight helps row-level safety (RLS) that restricts which information rows every person or group can see. RLS is configured by way of dataset guidelines, that are a permissions dataset that maps customers or teams to the sector values they’ll entry.
For instance, a regional gross sales dashboard may be configured in order that:
- The EMEA gross sales group solely sees rows the place
area = 'EMEA'. - The NA gross sales group solely sees rows the place
area = 'NA'. - The VP of Gross sales sees all rows.
RLS guidelines are evaluated primarily based on the person’s identification as decided by IAM Identification Heart, that means the identical identification federation that controls sign-in additionally governs data-level entry. This is applicable equally to conventional dashboard views and AI-powered pure language queries. The identical safety insurance policies limit what information the AI can reference when producing solutions.
Column-level safety
Along with row-level restrictions, Fast Sight helps column-level safety (CLS) to cover delicate columns from particular customers or teams. For instance, a dataset containing worker data would possibly limit the wage and SSN columns to solely the HR group, whereas different teams can nonetheless entry non-sensitive columns in the identical dataset.
How identification ties to personal connectivity
The identification layer and community layer work collectively:
- A person on the company community authenticates by way of your IdP → IAM Identification Heart → Fast.
- Their request reaches Fast by way of the VPC endpoint (the non-public community path; see VPC endpoints for person and API entry).
- Fast evaluates their identification to find out position, House entry, and RLS/CLS insurance policies.
- When Fast fetches information from an on-premises supply, it makes use of the VPC connection (ENIs in your VPC; see VPC connections for information supply entry) to achieve the database over Direct Join.
- The response is returned to the person by way of the identical non-public path.
Other than the sign-in and static-asset visitors described underneath Enabling entry to required exterior domains, no visitors traverses the general public web, and at each level the person’s identification determines what they’ll see and do.
Validation and testing
Earlier than implementing restrictions in manufacturing, validate end-to-end connectivity for every entry sample:
| Entry sample | Take a look at | Anticipated outcome |
| Web site (VPC endpoint) | nslookup from the company community |
Resolves to a personal IP in your VPC CIDR |
| Web site (auth) | Navigate to the Fast console from a company machine | Signal-in completes through IdP. Console masses usually |
| API (VPC endpoint) | aws quicksight describe-account-settings from inside the VPC |
Returns account settings; Circulate Logs present supply IP out of your VPC |
| Information supply (VPC connection) | Create a take a look at Fast Sight information supply pointing to an on-premises database by way of the VPC connection | Connection take a look at succeeds. Take a look at question returns information |
| Information base (VPC connection) | Create a information base from an Amazon Redshift supply utilizing the VPC connection, then set off a sync | Sync completes. Content material seems within the information base |
| Motion connector (VPC connection) | Create a take a look at motion pointing to an inner API and invoke it by way of an agent | Motion returns the anticipated response |
| Embedded dashboards | Load an embedded Fast Sight dashboard from an inner app | Dashboard renders. Browser dev instruments verify non-public IP |
Monitoring
For ongoing visibility, allow VPC Circulate Logs on all endpoint and VPC connection ENIs to seize visitors metadata. Monitor CloudWatch metrics on VPC endpoints (ActiveConnections, BytesProcessed, PacketsDropped) and set alarms for connection failures or sudden visitors sources. These logs additionally function the audit path referenced in your compliance documentation.
Troubleshooting frequent points
| Symptom | Possible trigger | Decision |
| Fast web site unreachable from company community | DNS not resolving to VPC endpoint | Confirm the A document for |
| Locked out after enabling restrictions | Your IP/endpoint not within the permit checklist | Use the update-ip-restriction CLI command with an IAM identification that has API entry (the API just isn’t restricted by IP/VPC guidelines) so as to add your endpoint. |
| API calls timing out | Safety group blocking visitors | Ensure that the endpoint safety group permits inbound HTTPS (port 443) out of your company CIDR. |
| Information supply connection fails | VPC connection ENIs can’t attain goal | Confirm safety teams on the VPC connection ENIs permit outbound to the database port, and the database safety group permits inbound from the Fast safety group. For connections created earlier than April 27, 2023, confirm the inbound all-ports return-traffic rule. Examine route tables for a path to the on-premises community. |
| Static belongings not loading (clean web page) | Exterior domains blocked | Ensure that your proxy or NAT gateway permits *.cloudfront.web, and that *.s3. is reachable by way of an S3 VPC endpoint or your proxy. |
| SSO login fails | Signal-in domains unreachable | Enable signin.aws.amazon.com and |
| VPC connection standing reveals UNAVAILABLE | Execution position misconfigured | Confirm the execution position has ec2:CreateNetworkInterface, ec2:DescribeSubnets, ec2:DescribeSecurityGroups, ec2:ModifyNetworkInterfaceAttribute, and ec2:DeleteNetworkInterface, and that its belief coverage permits quicksight.amazonaws.com. |
| Public embedded dashboards inaccessible | VPC endpoint restrictions block public visitors | Identified habits: public embeds require VPC endpoint entry as soon as restrictions are enabled. Contemplate a separate endpoint for public shoppers, or disable public embedding. |
Safety greatest practices
Neither community isolation nor identification controls alone is adequate. This structure depends on each: community controls forestall unauthorized entry paths, whereas identification controls forestall unauthorized information entry inside licensed classes. The practices beneath preserve each layers.
- Least-privilege endpoint insurance policies: Limit web site endpoints by
aws:PrincipalAccountoraws:OrgId. On API endpoints, scope insurance policies to solely the precise actions your automation requires slightly than permitting allquicksight:*actions. - Layered safety teams: Apply safety teams to each VPC endpoint ENIs (person visitors) and VPC connection ENIs (information visitors). On endpoint ENIs, limit inbound HTTPS to your company CIDR ranges. On VPC connection ENIs, use a devoted safety group, limit outbound to solely the database ports and locations Fast wants, and reference that safety group in every information supply’s inbound guidelines.
- Allow VPC Circulate Logs on all endpoint ENIs: These logs seize visitors metadata for safety monitoring, anomaly detection, and compliance auditing. Additionally they present the audit path that regulatory frameworks require for managed community boundaries.
- Audit endpoint insurance policies often: Overview endpoint insurance policies quarterly. Use AWS Config guidelines to detect drift out of your baseline configuration.
- Separate VPC connections by sensitivity: In case you have a number of information environments (dev, staging, manufacturing), create separate VPC connections with distinct safety teams to forestall cross-environment entry.
- Monitor with CloudWatch: Set alarms on
PacketsDroppedandActiveConnectionsmetrics. Uncommon patterns might point out misconfiguration or tried unauthorized entry.
Instance Necessities and AWS Configuration
The next examples present how the configuration on this submit can deal with frequent safety community necessities. Consider them towards your individual necessities along with your safety workforce.
| Requirement | AWS controls that may help your evaluation |
| Delicate information should not traverse the general public web | VPC endpoints for person visitors, VPC connections for information visitors, and VPC Circulate Logs for community visibility |
| Person information isolation | Safety teams on VPC connection ENIs and row-level safety for delicate information entry |
| Entry restricted to licensed endpoints | VPC endpoint restrictions (Part 4), CloudTrail API logs and VPC Circulate Logs |
Price concerns
| Part | Price mannequin | Estimate |
| VPC interface endpoints | $0.01/hour per AZ + $0.01/GB processed | ~$7.20/month per endpoint per AZ (fastened) + information switch |
| VPC gateway endpoints (S3) | No cost | No cost |
| VPC connections (Fast ENIs) | Included with Fast Enterprise | No extra cost |
| NAT gateway (for exterior domains) | $0.045/hour + $0.045/GB processed | ~$32/month (fastened) + information switch |
| VPC Circulate Logs | CloudWatch Logs ingestion charges | Varies with visitors quantity |
| Direct Join | Port hours + information switch | Varies with circuit dimension |
Price optimization suggestions:
- Use gateway endpoints (no extra cost) for S3 as a substitute of interface endpoints the place doable.
- Consolidate endpoint ENIs: every endpoint solely wants ENIs within the AZs the place the Amazon Fast VPC connection subnets reside.
- Allow VPC Circulate Logs selectively on endpoint ENIs slightly than your complete VPC.
- Contemplate whether or not all exterior domains want NAT gateway entry or whether or not a focused proxy can be less expensive on your visitors patterns.
Conclusion
This structure establishes 4 complementary controls: VPC endpoints hold person visitors non-public, VPC connections give Fast a personal path to your information sources, identification federation determines who can entry what, and VPC endpoint restrictions make the non-public path necessary. Every layer is independently auditable and maps to particular compliance necessities (see Compliance mapping).
With this in place, Fast Brokers can question your on-premises databases, Fast Analysis can examine enterprise sources behind the firewall, Fast Sight dashboards can visualize delicate information, and Fast Flows can orchestrate inner methods, all with out your information traversing the general public web. The AI capabilities are unchanged. The publicity is eliminated.
To implement, begin with the VPC endpoints for person and API entry, and validate person entry earlier than progressing to the VPC connections for information supply entry. Allow VPC endpoint restrictions solely after confirming all entry patterns work by way of the non-public path. For identification federation setup and superior RLS/CLS configuration, discuss with the IAM Identification Heart documentation.
In regards to the authors