
Claude Desktop on Amazon Bedrock offers highly effective AI help, however with out built-in internet search, responses are restricted to the mannequin’s coaching data cutoff. Once you want present info, comparable to latest documentation updates, stay pricing, or climate updates, the mannequin can’t retrieve it by itself.
Amazon Bedrock AgentCore is a platform to construct, join, and optimize brokers at scale, with any framework or mannequin. With AgentCore Gateway, a functionality of Amazon Bedrock AgentCore, you’ll be able to shut this data cutoff hole by connecting Claude Desktop to Net Search. Net Search is a totally managed, Mannequin Context Protocol (MCP)-compatible internet search functionality backed by an Amazon internet index that spans tens of billions of paperwork. All question site visitors stays inside AWS infrastructure, with no exterior API keys to handle and no queries leaving your boundary.
With Claude Desktop, you should utilize managed MCP servers to connect with an AgentCore Gateway with the Net Search goal enabled. On this publish, we stroll by the steps to arrange this integration and use JSON Net Token (JWT)-based inbound authentication to safe the communication.
Structure
Many enterprises working on AWS use AWS IAM Identification Middle for single sign-on (SSO) entry to their AWS accounts. On this walkthrough, we use AWS IAM Identification Middle because the authentication supply for the AgentCore Gateway. With this setup, Claude Desktop on Amazon Bedrock can invoke Net Search by a trusted, enterprise-managed id circulate. This method aligns with current organizational id governance. No separate credentials or third-party id suppliers are required.
To bridge AWS IAM Identification Middle with the AgentCore Gateway JWT-based authentication, we use Amazon Cognito as a federation layer with the OAuth 2.0 authorization code grant circulate. IAM Identification Middle handles person authentication by Safety Assertion Markup Language (SAML). Amazon Cognito points JWTs, and the AgentCore Gateway validates them on every request. The complete authentication chain stays inside AWS.
The next sequence diagram illustrates this authentication circulate.
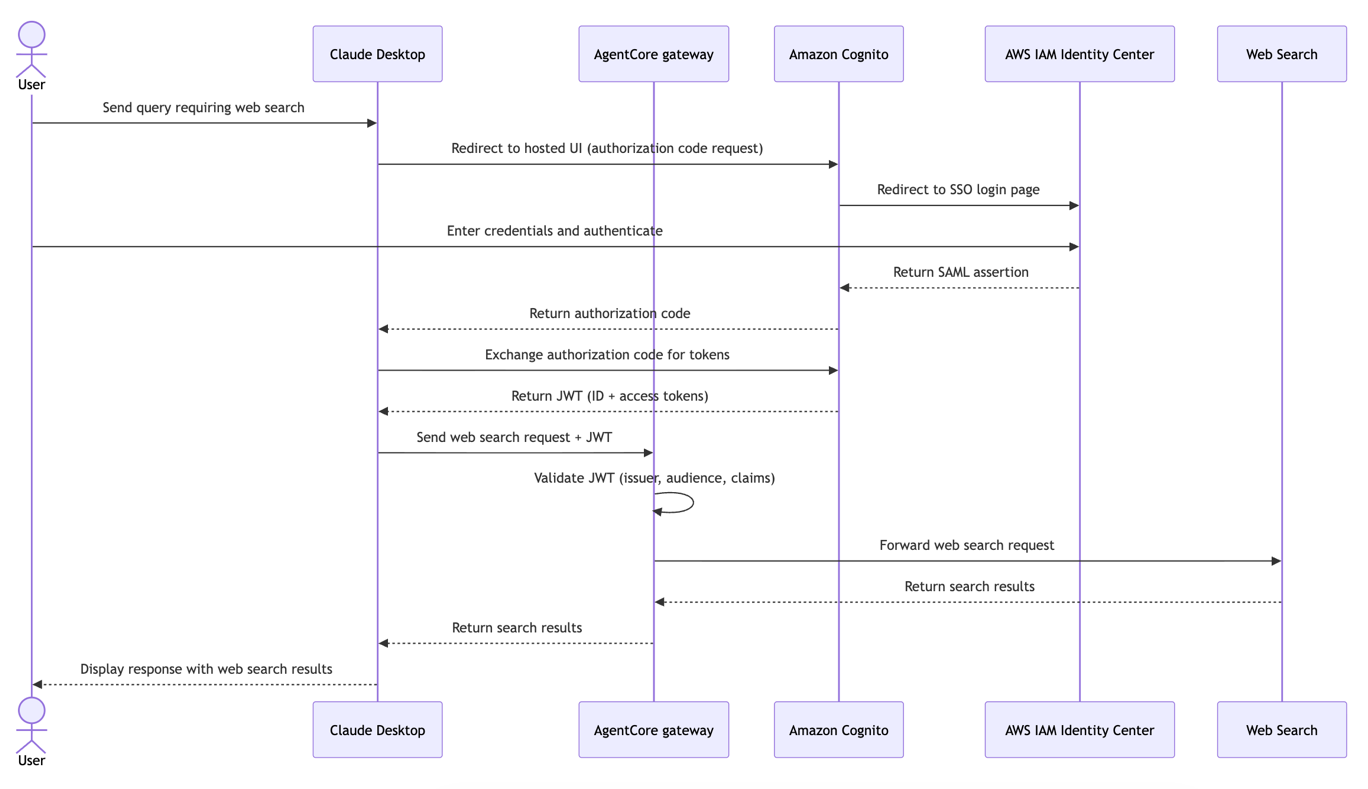
Determine 1: Person authentication and authorization sequence diagram
Stipulations
To comply with together with the steps on this publish, you want the next:
- An AWS account with permissions to create AWS Identification and Entry Administration (IAM) roles and Amazon Bedrock AgentCore sources.
- Admin entry to your administration account in AWS Organizations (for AWS IAM Identification Middle configuration).
- AWS IAM Identification Middle preconfigured for SSO entry to AWS accounts.
- Claude Desktop arrange with Amazon Bedrock because the inference supplier.
- The AWS Command Line Interface (AWS CLI) v2 put in and configured.
- Python 3.10 or later.
- The Boto3 SDK up to date to the newest model.
Net Search on Amazon Bedrock AgentCore is at present out there within the US East (N. Virginia) AWS Area (us-east-1), Europe (Eire) Area (eu-west-1), and Asia Pacific (Tokyo) Area (ap-northeast-1). Confirm that your gateway is created in considered one of these Areas.
Configuration
The configuration entails organising the authentication chain (AWS IAM Identification Middle to Amazon Cognito to JWT) after which wiring the AgentCore Gateway into Claude Desktop. We stroll by every step within the following part.
Step 1: Create an Amazon Cognito person pool
In your goal AWS account, create an Amazon Cognito person pool that may function the OpenID Join (OIDC) token issuer for the AgentCore Gateway.
Save these values for later steps:
- Person Pool ID:
$USER_POOL_ID. - Area:
.auth. .amazoncognito.com - Viewers:
urn:amazon:cognito:sp:. - ACS URL:
https://..auth. .amazoncognito.com/saml2/idpresponse
Step 2: Configure IAM Identification Middle SAML utility
In your AWS Organizations administration account, create a SAML utility that federates with Cognito:
- Open IAM Identification Middle console.
- Select Purposes, Add utility, I’ve an utility I wish to arrange, SAML 2.0, after which Subsequent.
- Fill within the following particulars:
- Show title: AgentCore Net Search.
- Choose Manually kind your metadata worth.
- ACS URL:
https://..auth. .amazoncognito.com/saml2/idpresponse - Viewers:
urn:amazon:cognito:sp:.
- ACS URL:
- Obtain the SAML metadata XML file and select Submit.
- After the applying is created, edit the attribute mappings and insert the next values:
- Topic, ${person:topic}, Format: Persistent.
- Electronic mail, ${person:electronic mail}, Format: Primary.
- Assign the customers or teams that might have entry to Net Search.
Step 3: Wire SAML IdP into Cognito
Again within the goal account, register IAM Identification Middle as a SAML id supplier in your Cognito person pool:
Step 4: Create Cognito app shopper for Amazon Bedrock AgentCore
Create an app shopper with a shopper secret. Claude Desktop makes use of this shopper to provoke the OAuth circulate, which authenticates the person by IAM Identification Middle and obtains a JWT for the AgentCore Gateway:
Be aware the Consumer ID and Consumer Secret from the output. These are your utility shopper ID and secret.
Step 5: Configure AgentCore Gateway with Net Search device
On this step, we create a brand new AgentCore Gateway with Inbound Auth Sort as JSON Net Tokens (JWT). For this configuration, we use the Cognito person pool ID and utility shopper ID that have been created within the prior steps.
Run the next Python script to create the gateway with the required configurations, changing all placeholders with precise values out of your setting.
You now have an AgentCore Gateway with Net Search device, with JWT-based inbound authorization.
Step 6: Configure Claude Desktop
Use the steps within the Claude Desktop configuration documentation to entry the configuration window for Claude Desktop with Amazon Bedrock. After you open it, select Connectors and Extensions, then select Add server, after which select Clean.
The next screenshot reveals the configuration window with these choices.
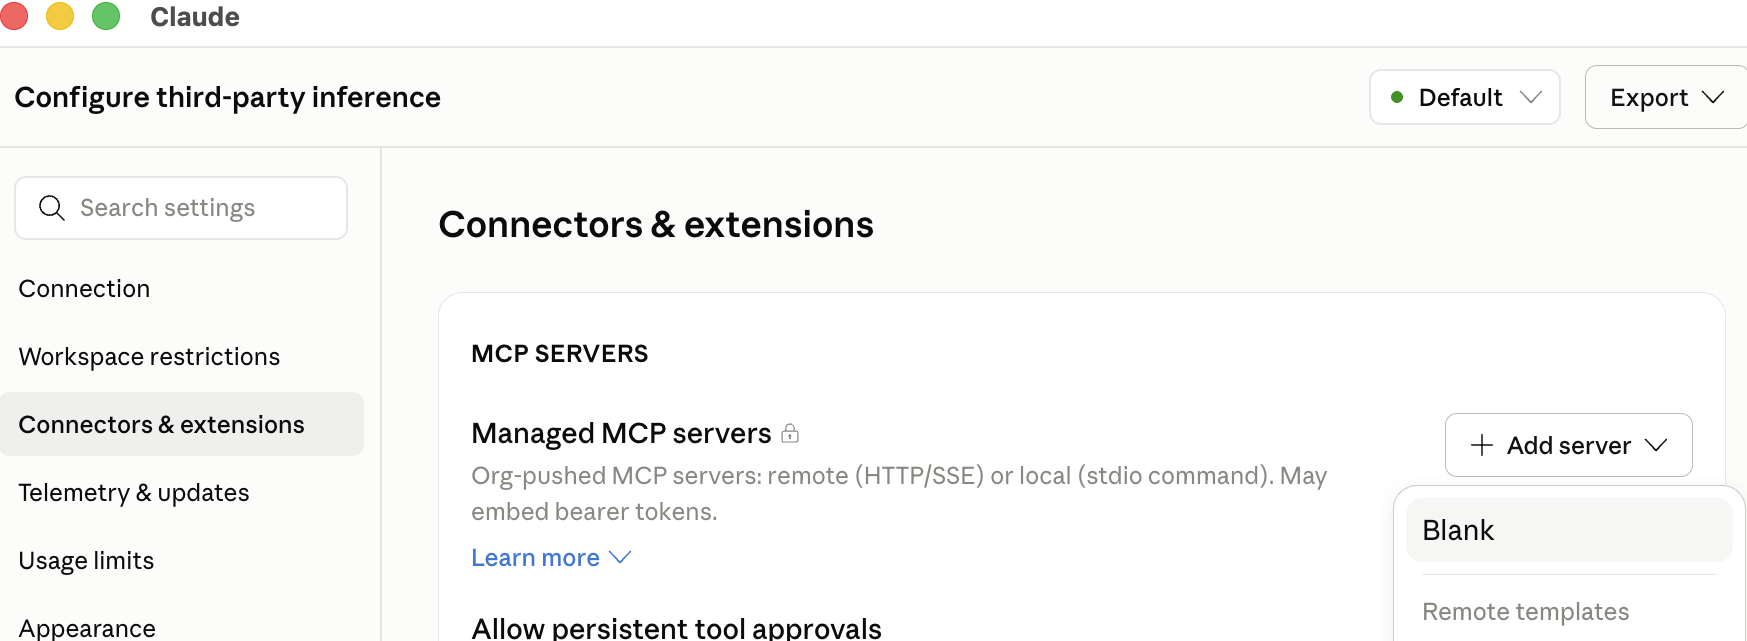
Determine 2: Claude Desktop connector configuration window
Enter the next particulars:
- Identify: websearchtool.
- Transport: Streamable HTTP.
- URL: Enter the gateway useful resource URL for the AgentCore Gateway created in Step 5.
- OAuth: Convey your individual shopper.
- Consumer ID: Enter the shopper ID for the app shopper created in Step 4.
- Consumer Secret: Enter the shopper secret for the app shopper created in Step 4.
- Authorization Server: Enter
["https://..auth. .amazoncognito.com/oauth2/authorize"] - Scope: openid.
- Callback host:
localhost. - Callback port: 53280.
Once you’re executed, select sign up and check. This could open a browser so that you can authenticate, redirecting you to your AWS IAM Identification Middle SSO login. Enter your credentials to authenticate. If profitable, you must see a message comparable to, “Authorization full. You possibly can shut this tab and return to Claude.”
Again in Claude Desktop, you must see a profitable MCP registration message like within the following picture.
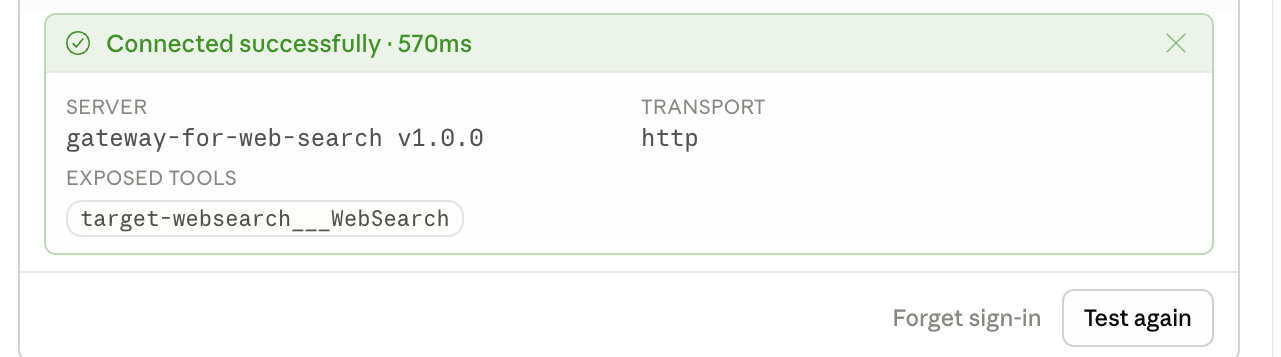
Determine 3: Profitable MCP server registration in Claude Desktop
Claude Desktop will now uncover the WebSearchTool by the MCP instruments/checklist name. It invokes the device mechanically each time the mannequin wants present info from the online.
Testing and validation
In your most popular interface (for instance, Chat or Cowork), ship a question that requires Claude Desktop to retrieve the newest outcomes. It’s best to see a device execution approval field, indicating that Claude has efficiently found the Net Search device. On approval, you must see the online search outcomes included within the response.
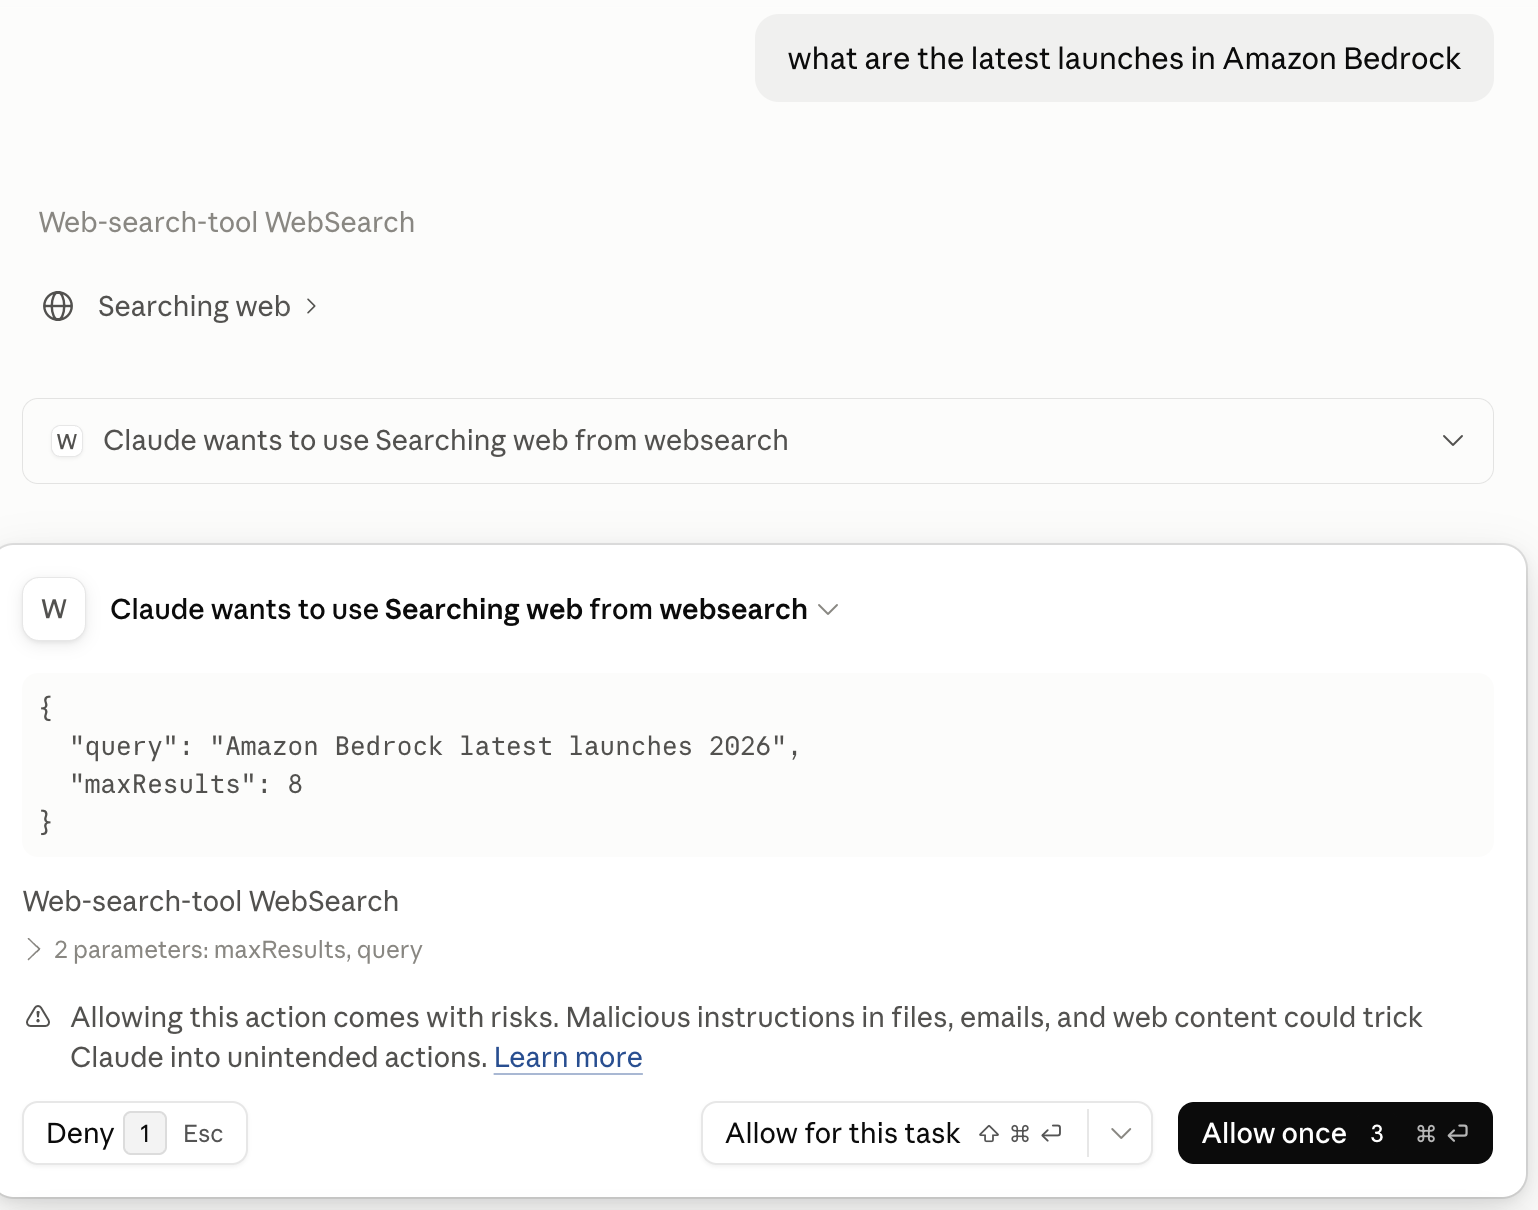
Determine 4: Net Search device execution approval dialog
The dialog reveals the question Claude needs to run and presents three choices: Deny, Permit for this job, or Permit as soon as. On approval, Net Search outcomes are included within the response.
Clear up
If you happen to created sources whereas following alongside, carry out the next steps to delete them:
Lastly, within the IAM Identification Middle console within the administration account, delete the SAML utility you created in Step 2.
Conclusion
On this publish, we walked by integrating Net Search on AgentCore with Claude Desktop. Whereas this walkthrough makes use of AWS IAM Identification Middle because the id supplier, the identical sample works with any SAML or OIDC-compatible id supplier. You possibly can substitute your current IdP by configuring it as a federation supply in Amazon Cognito. This method closes the online search hole with out introducing third-party dependencies, and all queries keep inside your AWS boundary.
To get began, comply with the steps above to arrange the combination in your individual setting. For superior gateway configurations, see the AgentCore Gateway Developer Information. To be taught extra about Net Search, see the Net Search documentation.
In regards to the creator